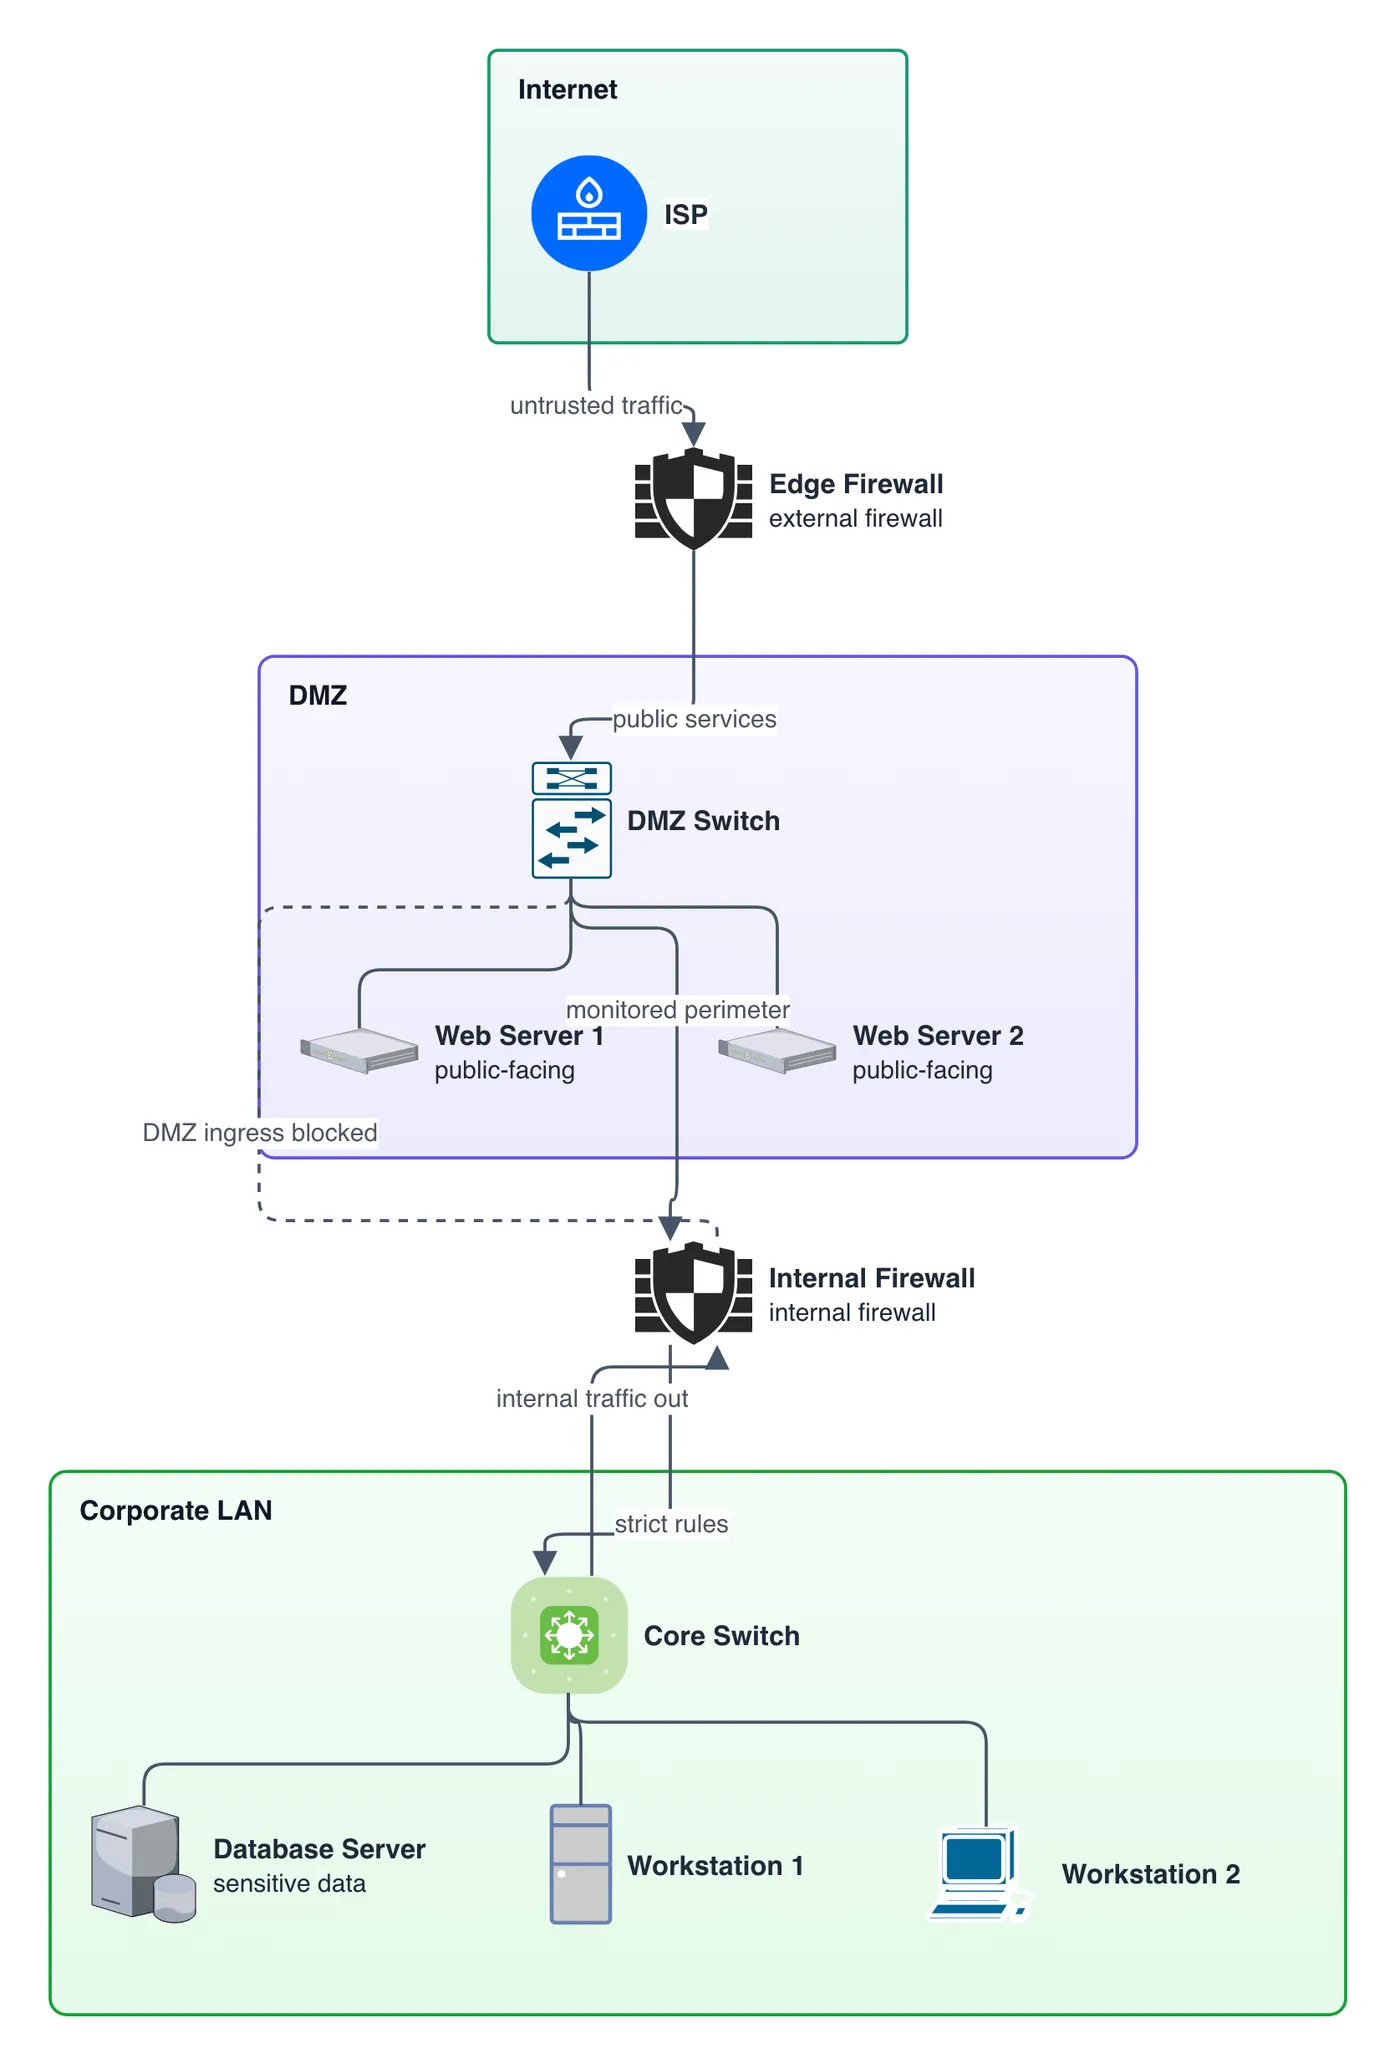
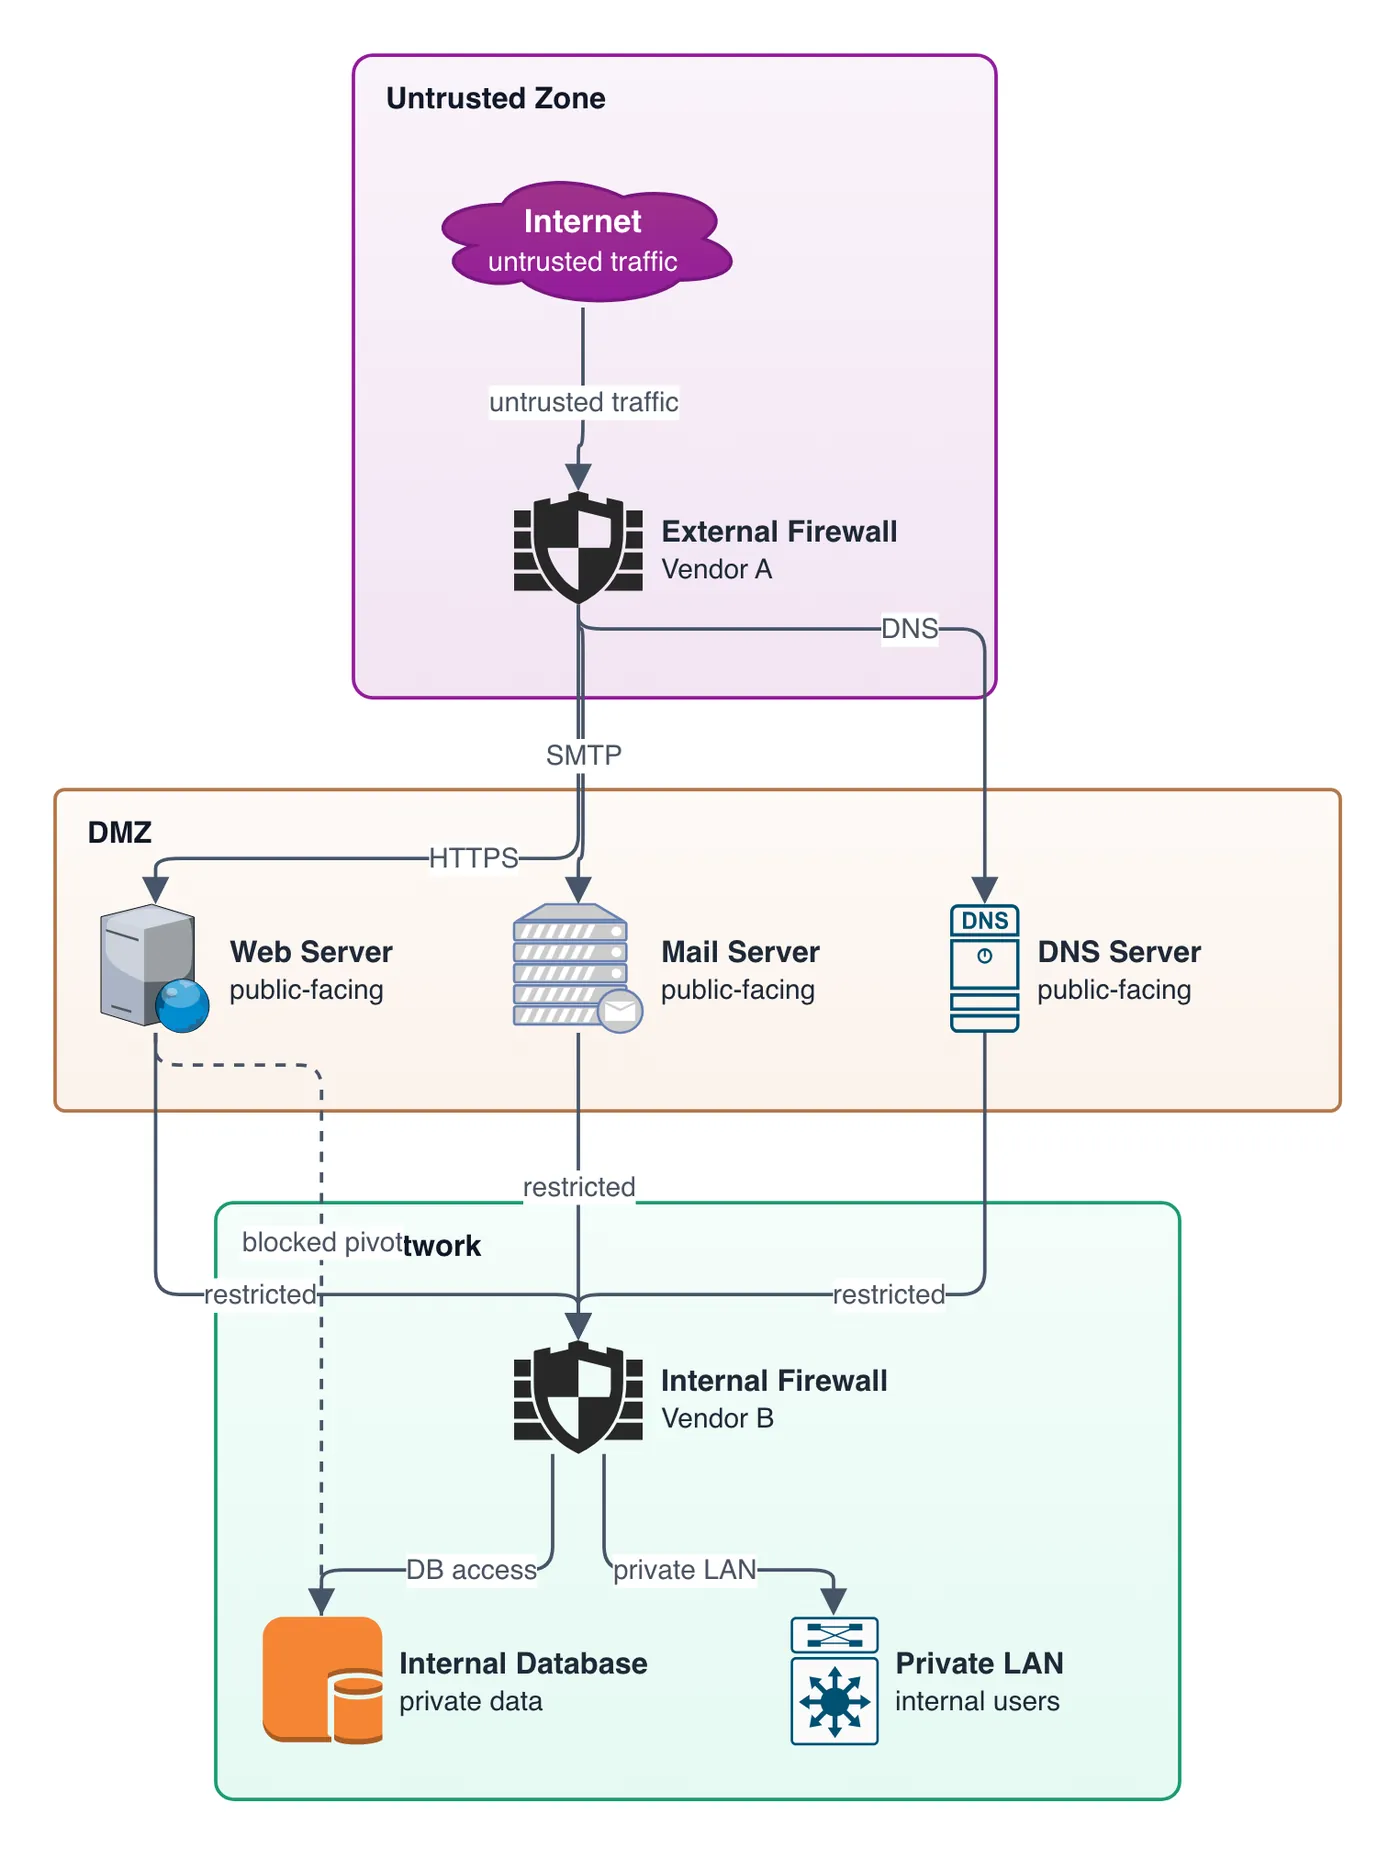
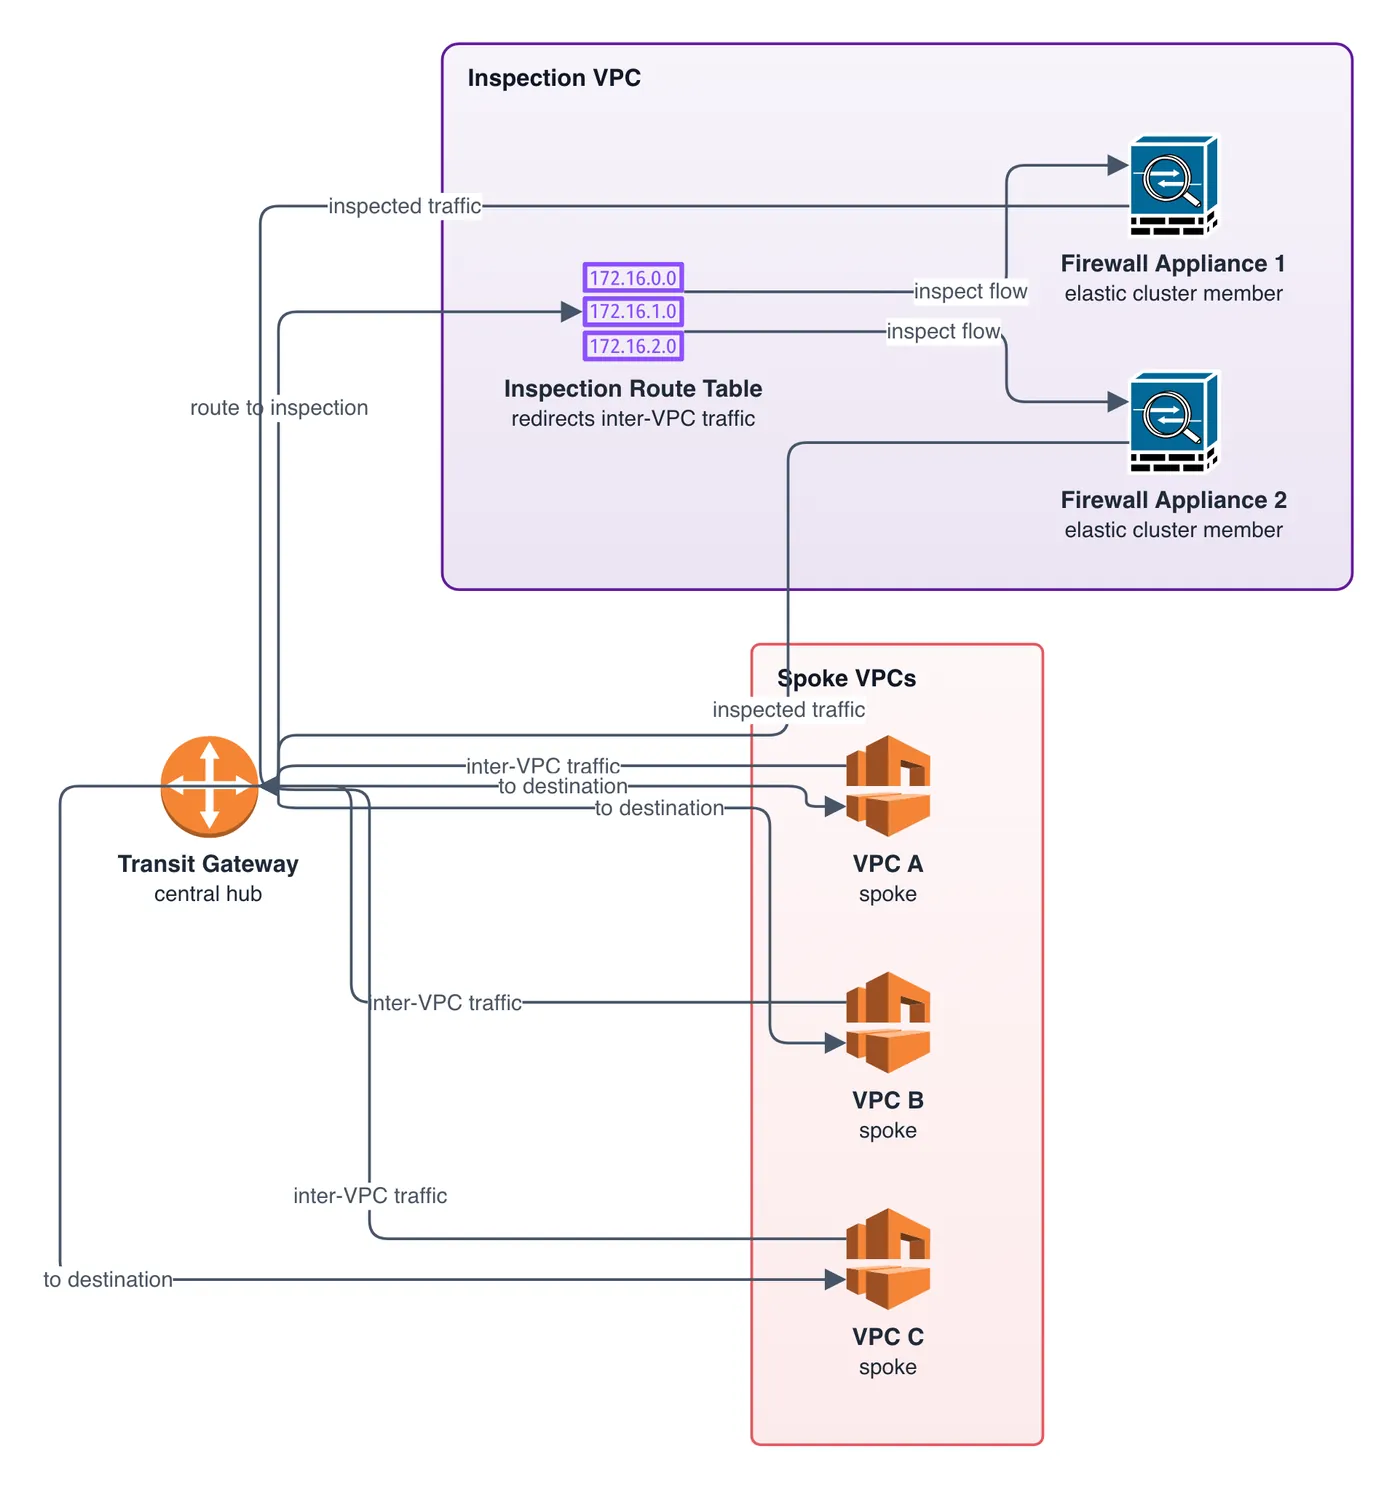
Centralized Cloud Firewall Inspection VPC
Network Design diagram · made in Skemio
What it shows
- A central Transit Gateway directs all inter-VPC traffic to inspection.
- Centralized firewall appliances inspect flows without per-VPC instances.
- Eliminates complex N*(N-1) mesh peering while enforcing zero-trust policies.
The takeaway
Route inter-VPC traffic through a dedicated inspection hub instead of messy mesh peering.
- #CloudArchitecture
- #AWS
- #NetworkSecurity
- #TransitGateway
- #DevOps
- #Infrastructure