Centralized Egress Inspection on AWS
Cloud Architecture diagram · made in Skemio
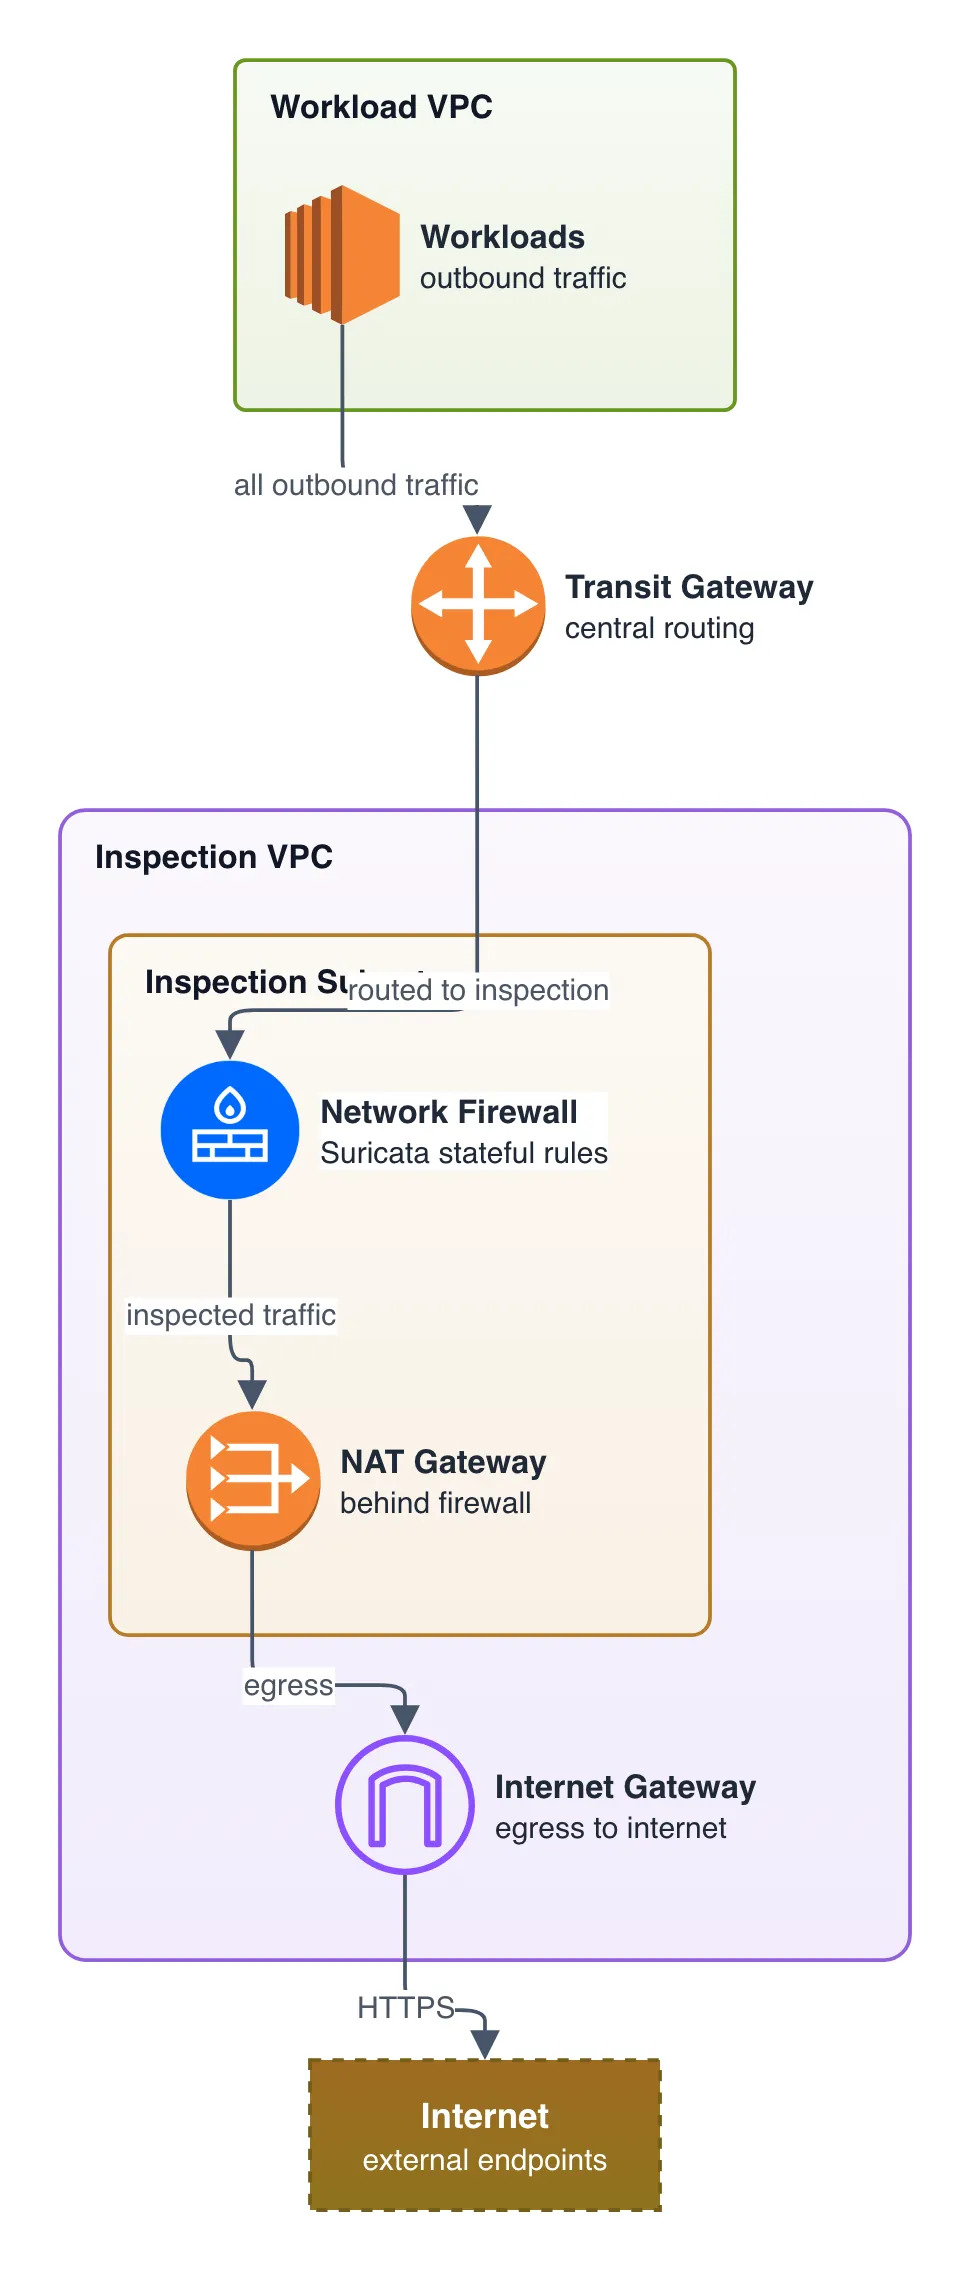
What it shows
- Routes 100% of outbound internet traffic through an inspection VPC.
- AWS Network Firewall enforces Suricata stateful rules and domain filtering.
- NAT Gateway sits behind the firewall to avoid bypassing threat checks.
The takeaway
Route all spoke egress through an inspected transit VPC to block malware, C2 callbacks, and data exfiltration.
- #CloudSecurity
- #AWS
- #DevSecOps
- #Networking
- #SystemDesign
- #InfoSec