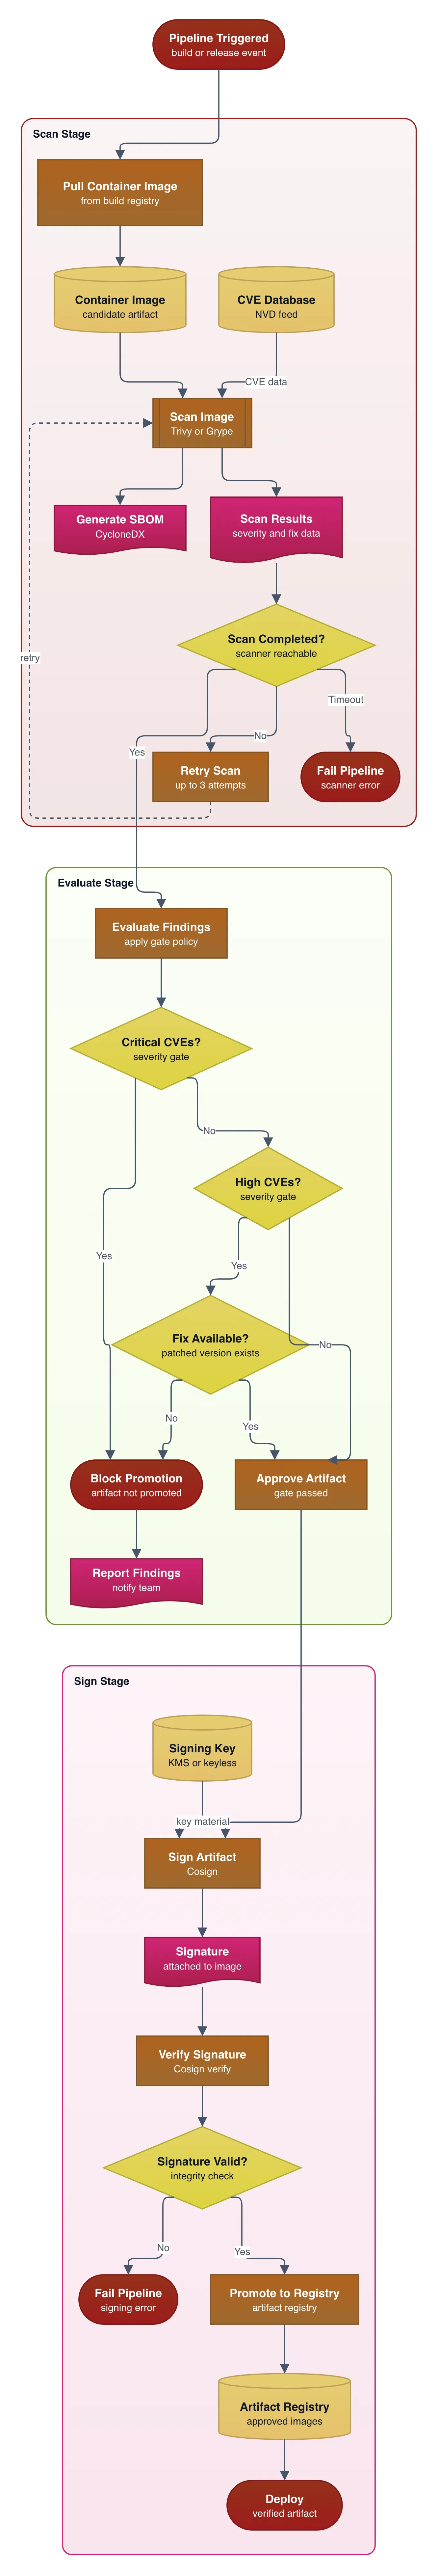
Container Image Vulnerability Scanning Gate
DevOps & CI/CD diagram · made in Skemio
What it shows
- Scan container images directly before promoting to artifact registries.
- Block the pipeline on critical or high severity CVEs with zero fixes.
- Sign approved artifacts with Cosign to guarantee deployment integrity.
The takeaway
Automated security gates at promotion block CVEs without slowing down engineering release cadence.
- #DevOps
- #DevSecOps
- #Docker
- #Kubernetes
- #CICD
- #Security