OAuth 2.0 Authorization Code Lifecycle
State Diagrams · made in Skemio
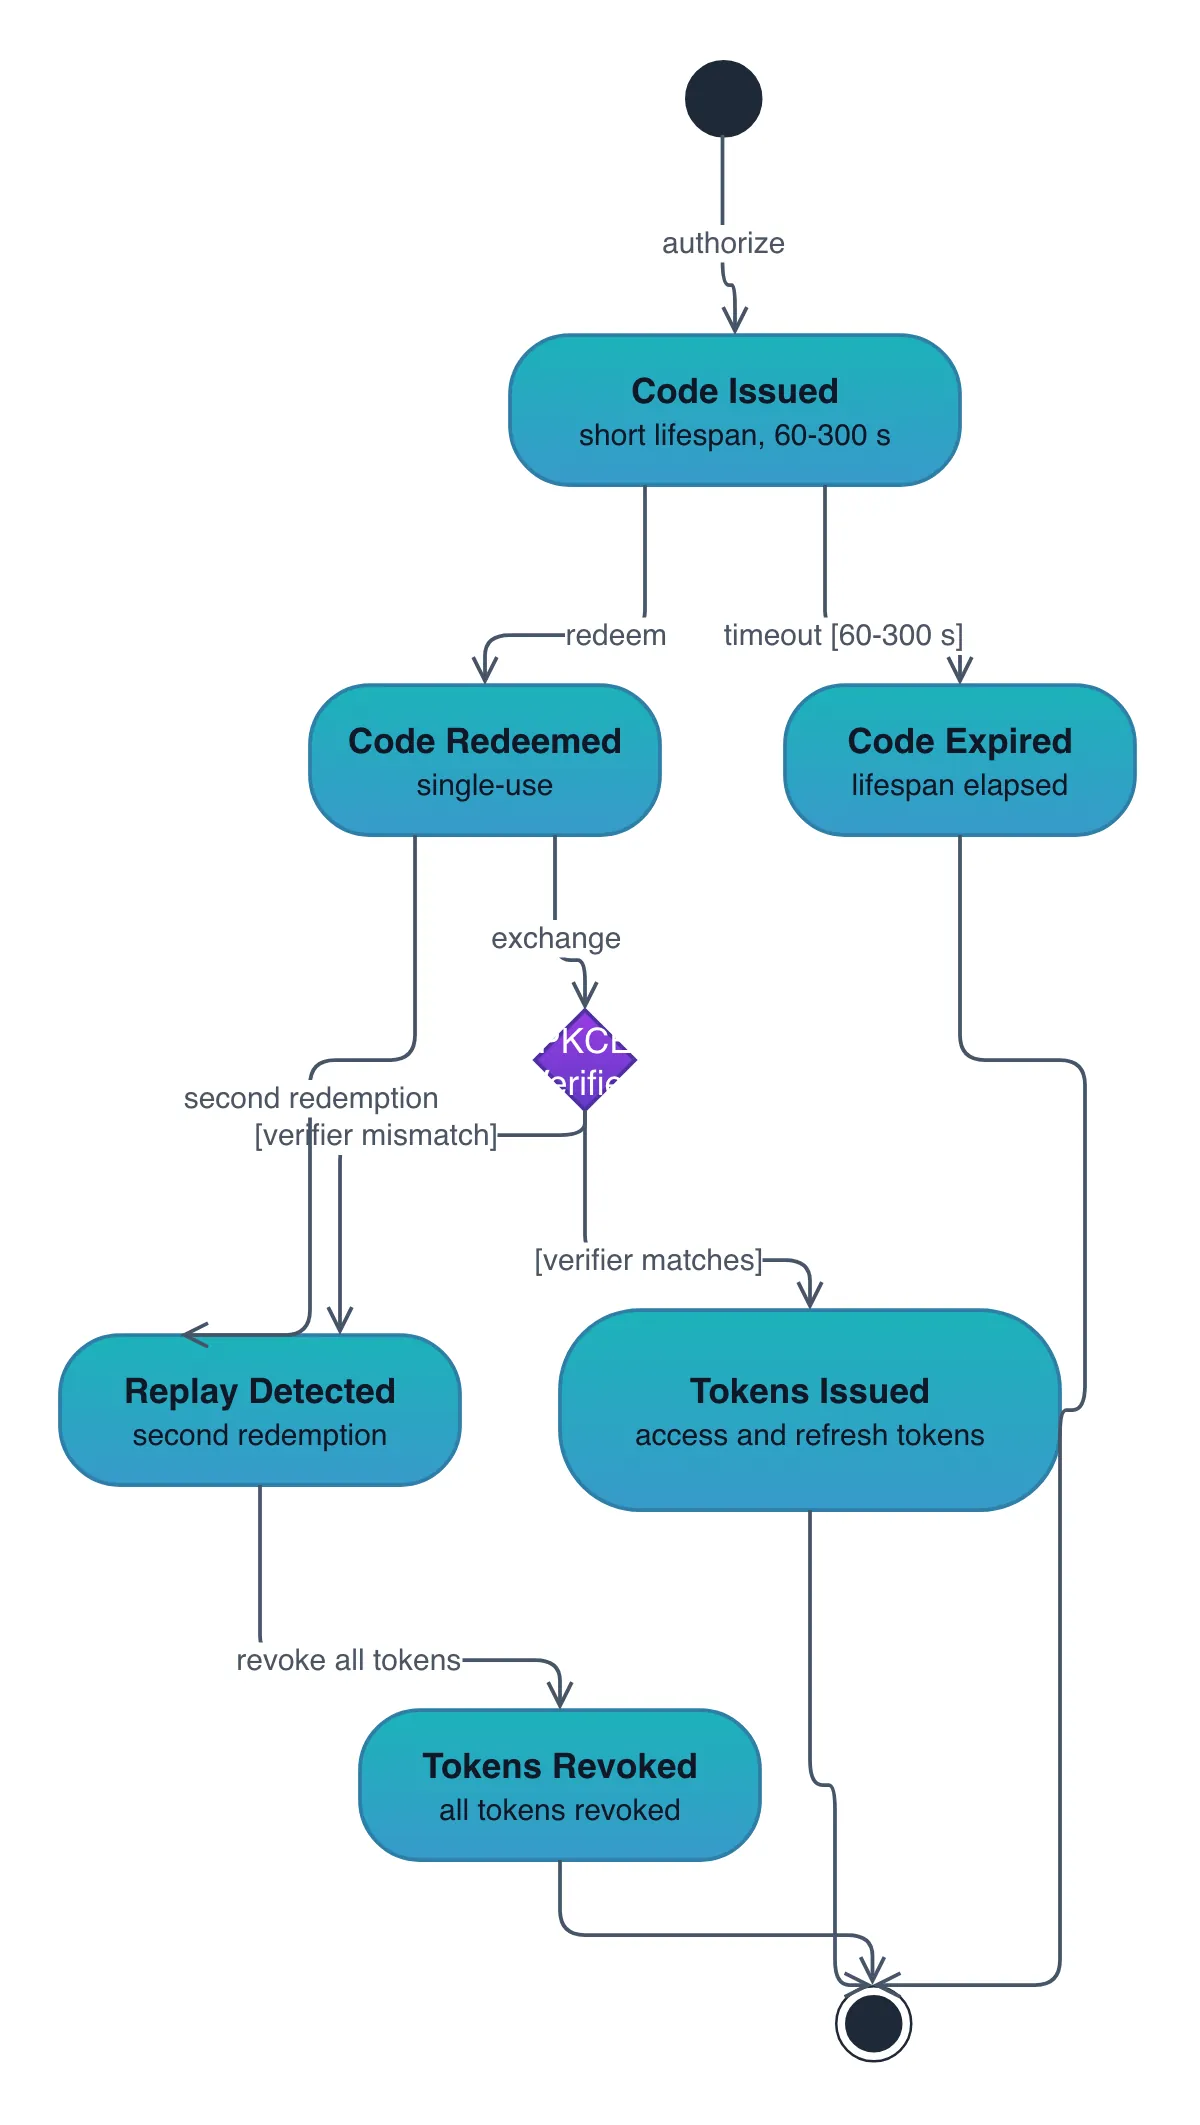
What it shows
- Authorization codes have short lifespans, typically 60 to 300 seconds
- Codes are strictly single-use; a second redemption revokes all tokens
- PKCE code verifiers mathematically tie the exchange to the original client
The takeaway
OAuth codes must be strictly single-use: replay attempts trigger automatic token revocation.
- #OAuth2
- #CyberSecurity
- #SystemDesign
- #WebSecurity
- #Authentication
- #BackendDev