Runtime Security with Falco & eBPF
DevOps & CI/CD diagram · made in Skemio
What it shows
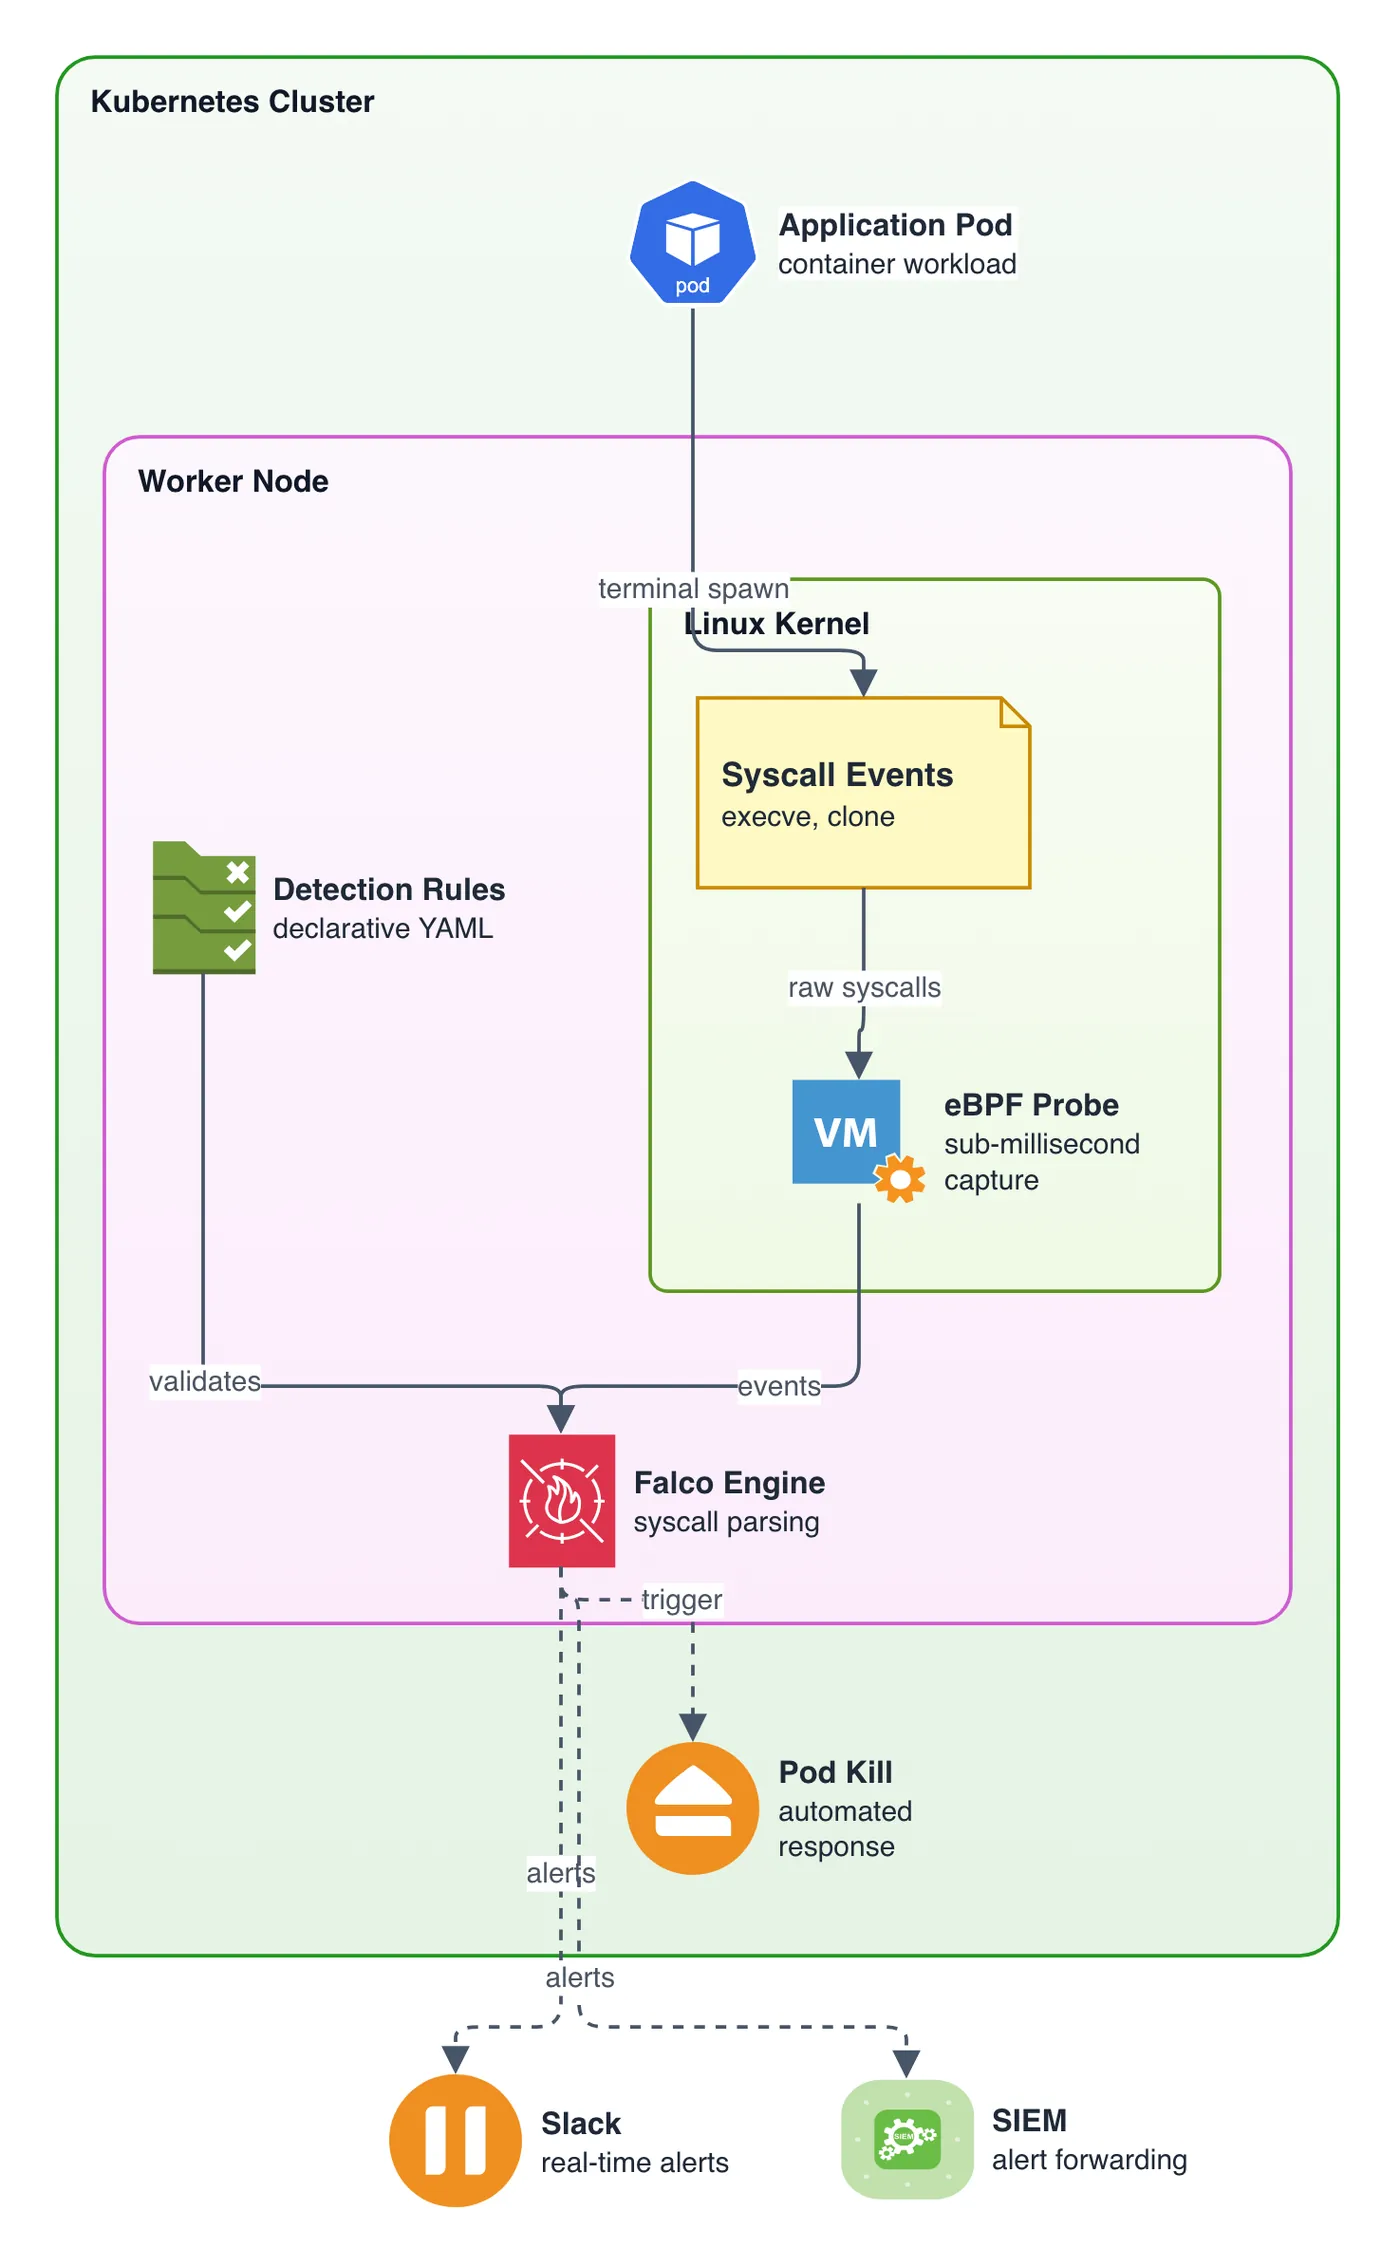
- Captures raw syscalls in the Linux kernel via eBPF with sub-millisecond lag
- Validates execution events against declarative YAML threat detection rules
- Dispatches real-time alerts to Slack, SIEM, or trigger automated pod kills
The takeaway
Kernel-level visibility detects runtime container intrusions without patching application code.
- #DevOps
- #Kubernetes
- #CloudSecurity
- #eBPF
- #ContainerSecurity
- #SRE