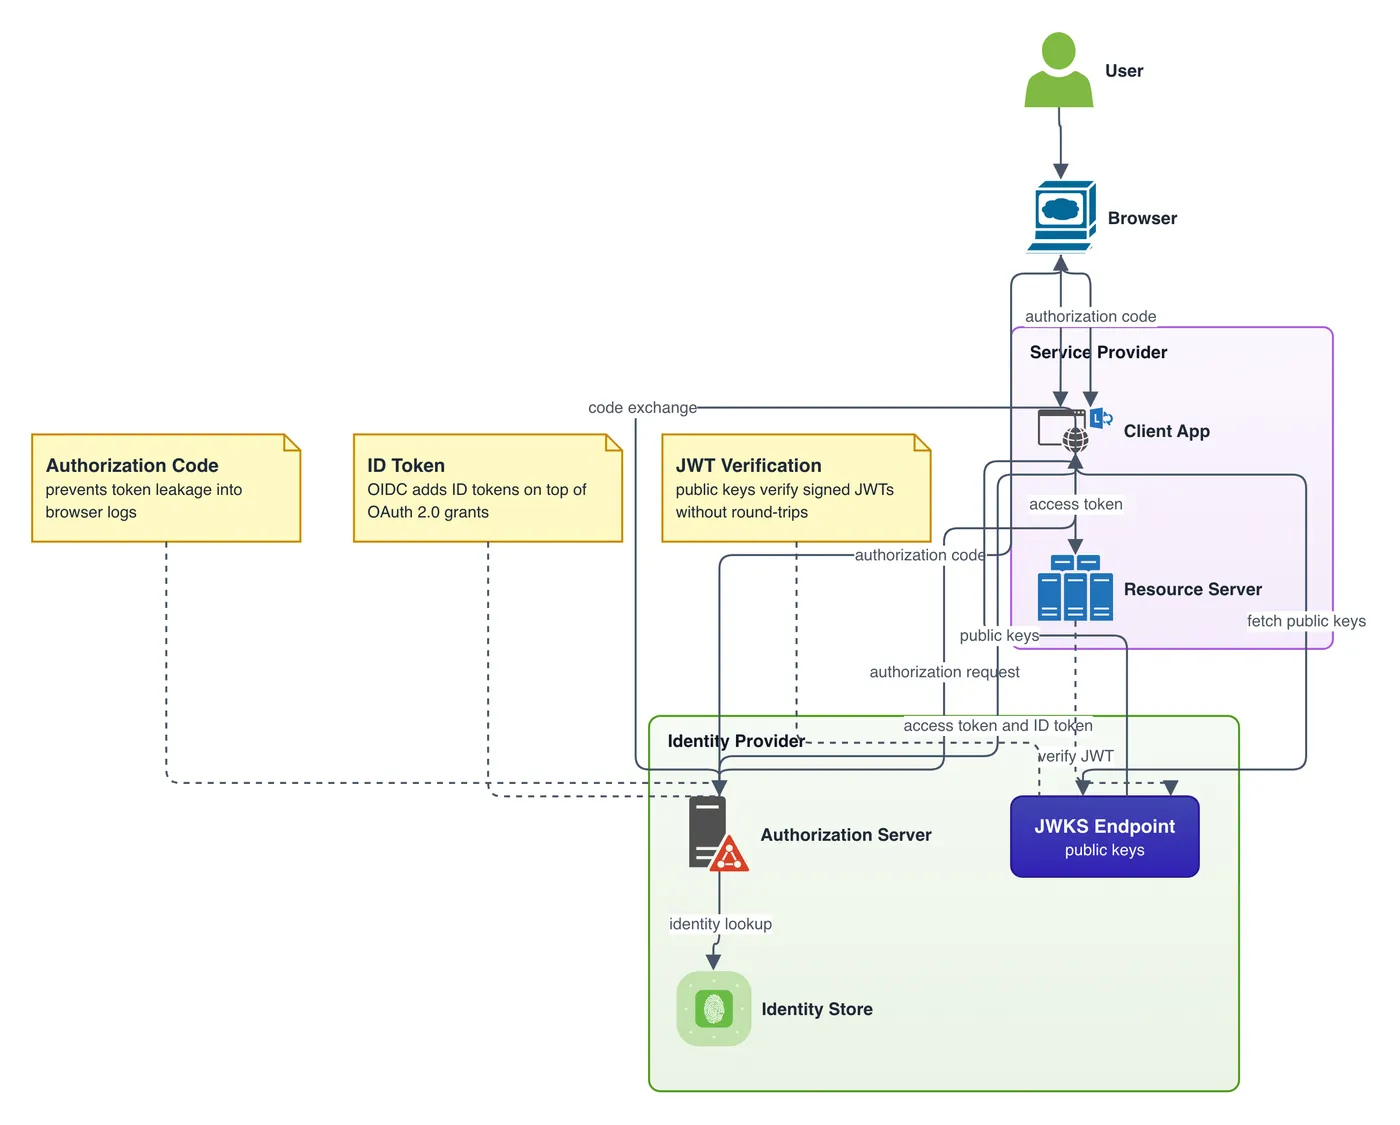
Single Sign-On Architecture with OAuth 2.0 & OIDC
System Design diagram · made in Skemio
What it shows
- Authorization code exchange prevents tokens from leaking into browser logs
- OpenID Connect adds ID tokens on top of OAuth 2.0 authorization grants
- Public keys verify cryptographically signed JWTs without round-trips
The takeaway
SSO decouples identity verification from access control using signed, short-lived tokens.
- #SystemDesign
- #Security
- #OAuth
- #Authentication
- #WebSecurity
- #Backend