Static vs Dynamic Analysis vs IAST
Venn Diagrams · made in Skemio
What it shows
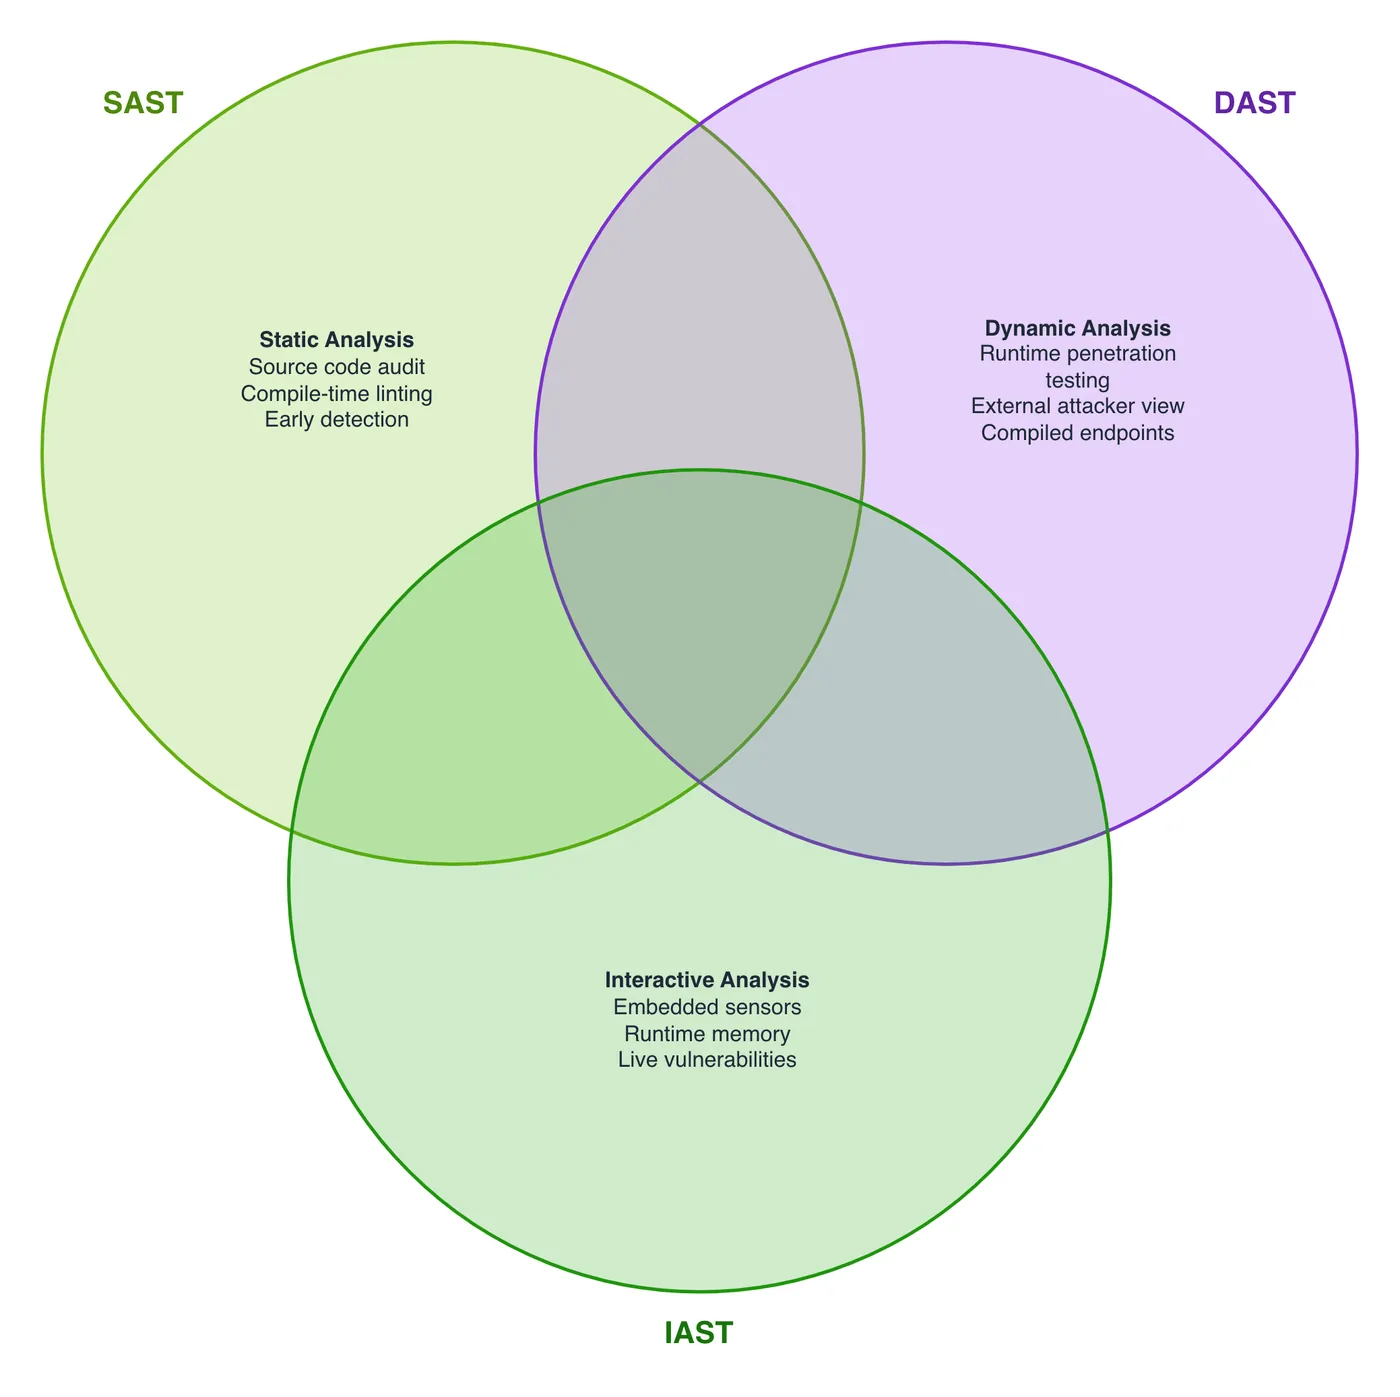
- SAST audits source code early without running the application.
- DAST tests compiled endpoints from outside like a real attacker.
- IAST embeds sensors into runtime memory to detect live vulnerabilities.
The takeaway
Use SAST in pull requests, DAST against test environments, and IAST to catch deep runtime vulnerabilities.
- #AppSec
- #CyberSecurity
- #DevSecOps
- #SoftwareEngineering
- #InfoSec
- #CodeQuality