Supply Chain Security with Cosign and SLSA
DevOps & CI/CD diagram · made in Skemio
What it shows
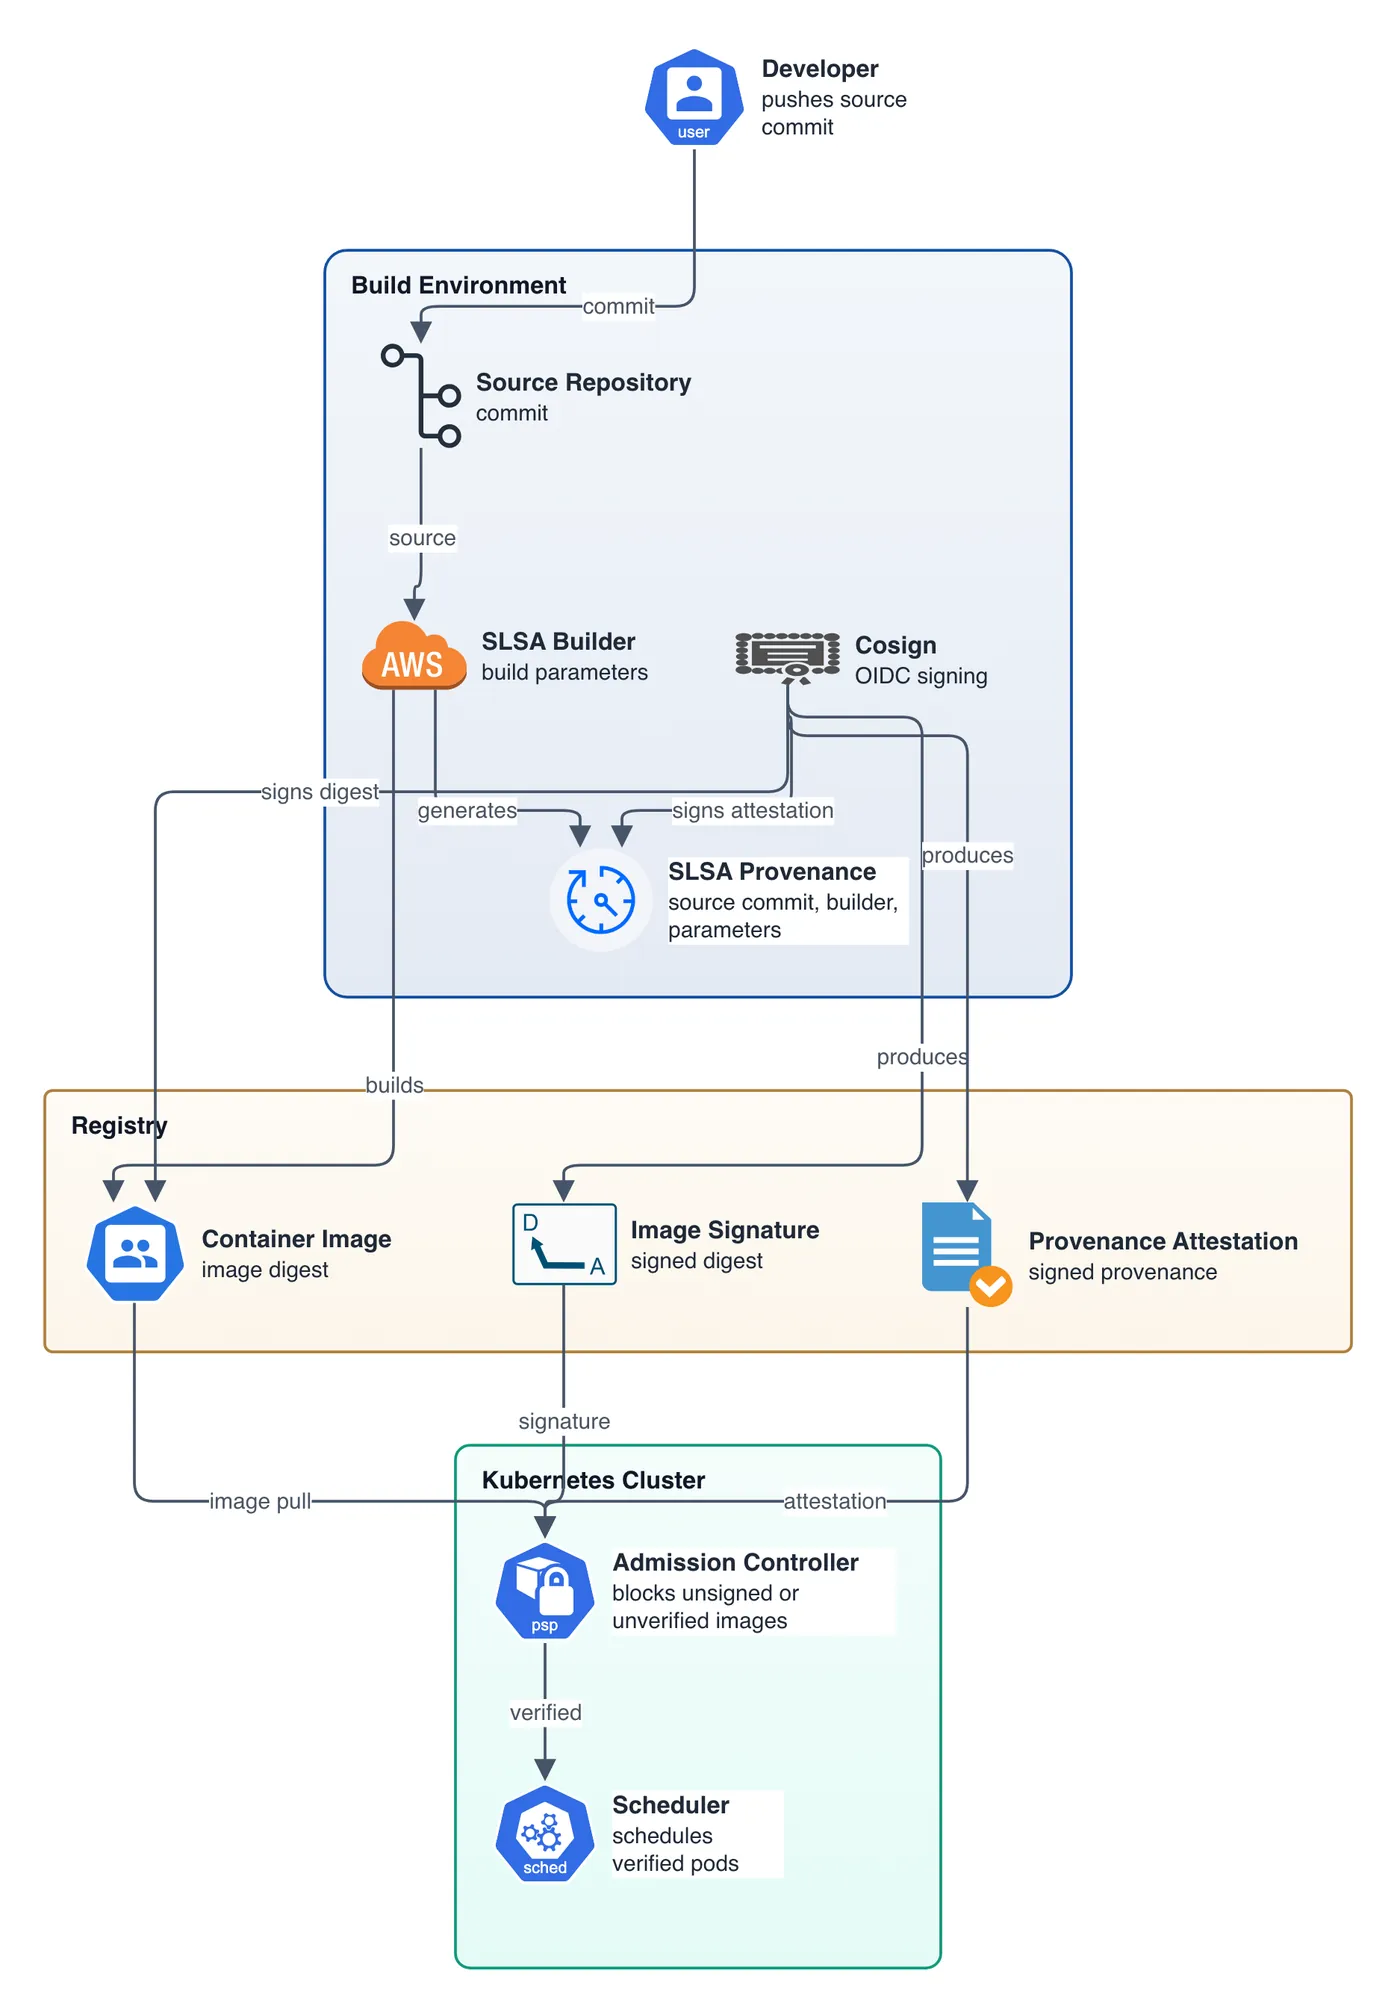
- SLSA provenance documents the source commit, builder, and build parameters.
- Cosign signs both the image digest and provenance attestations with OIDC.
- Admission controllers block unsigned and unverified images before scheduling.
The takeaway
Cryptographic signatures and SLSA attestations verify code authenticity before pods ever reach cluster nodes.
- #DevSecOps
- #Security
- #Kubernetes
- #Containers
- #CI_CD