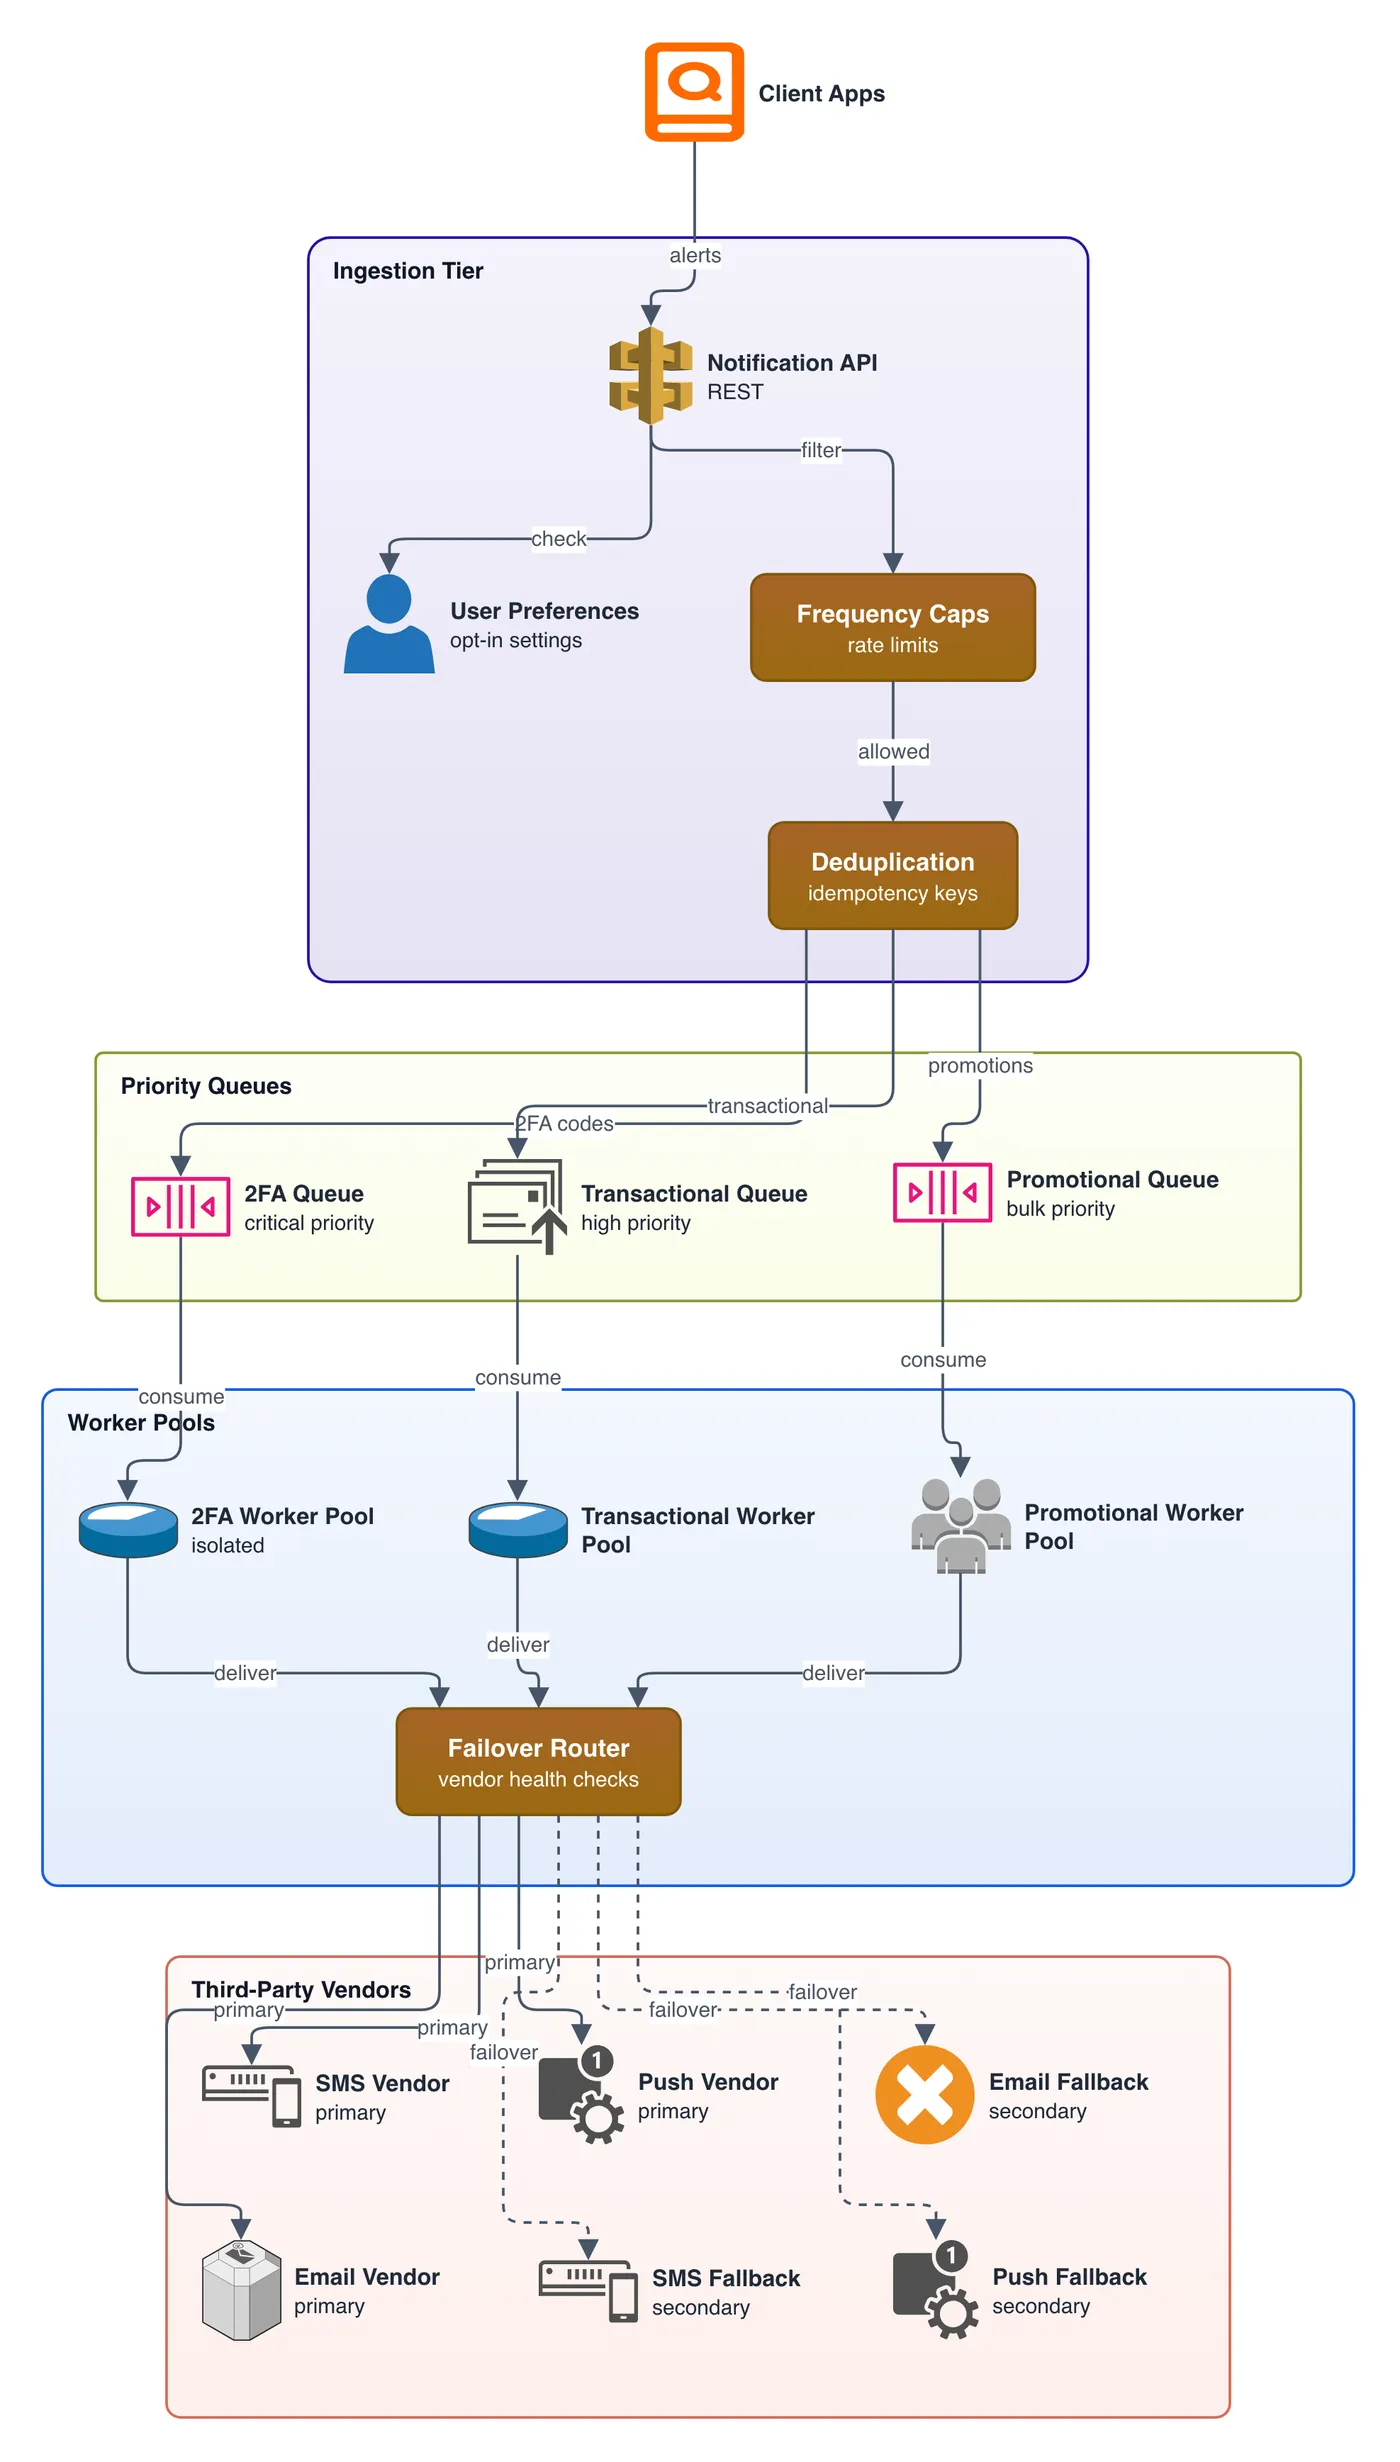
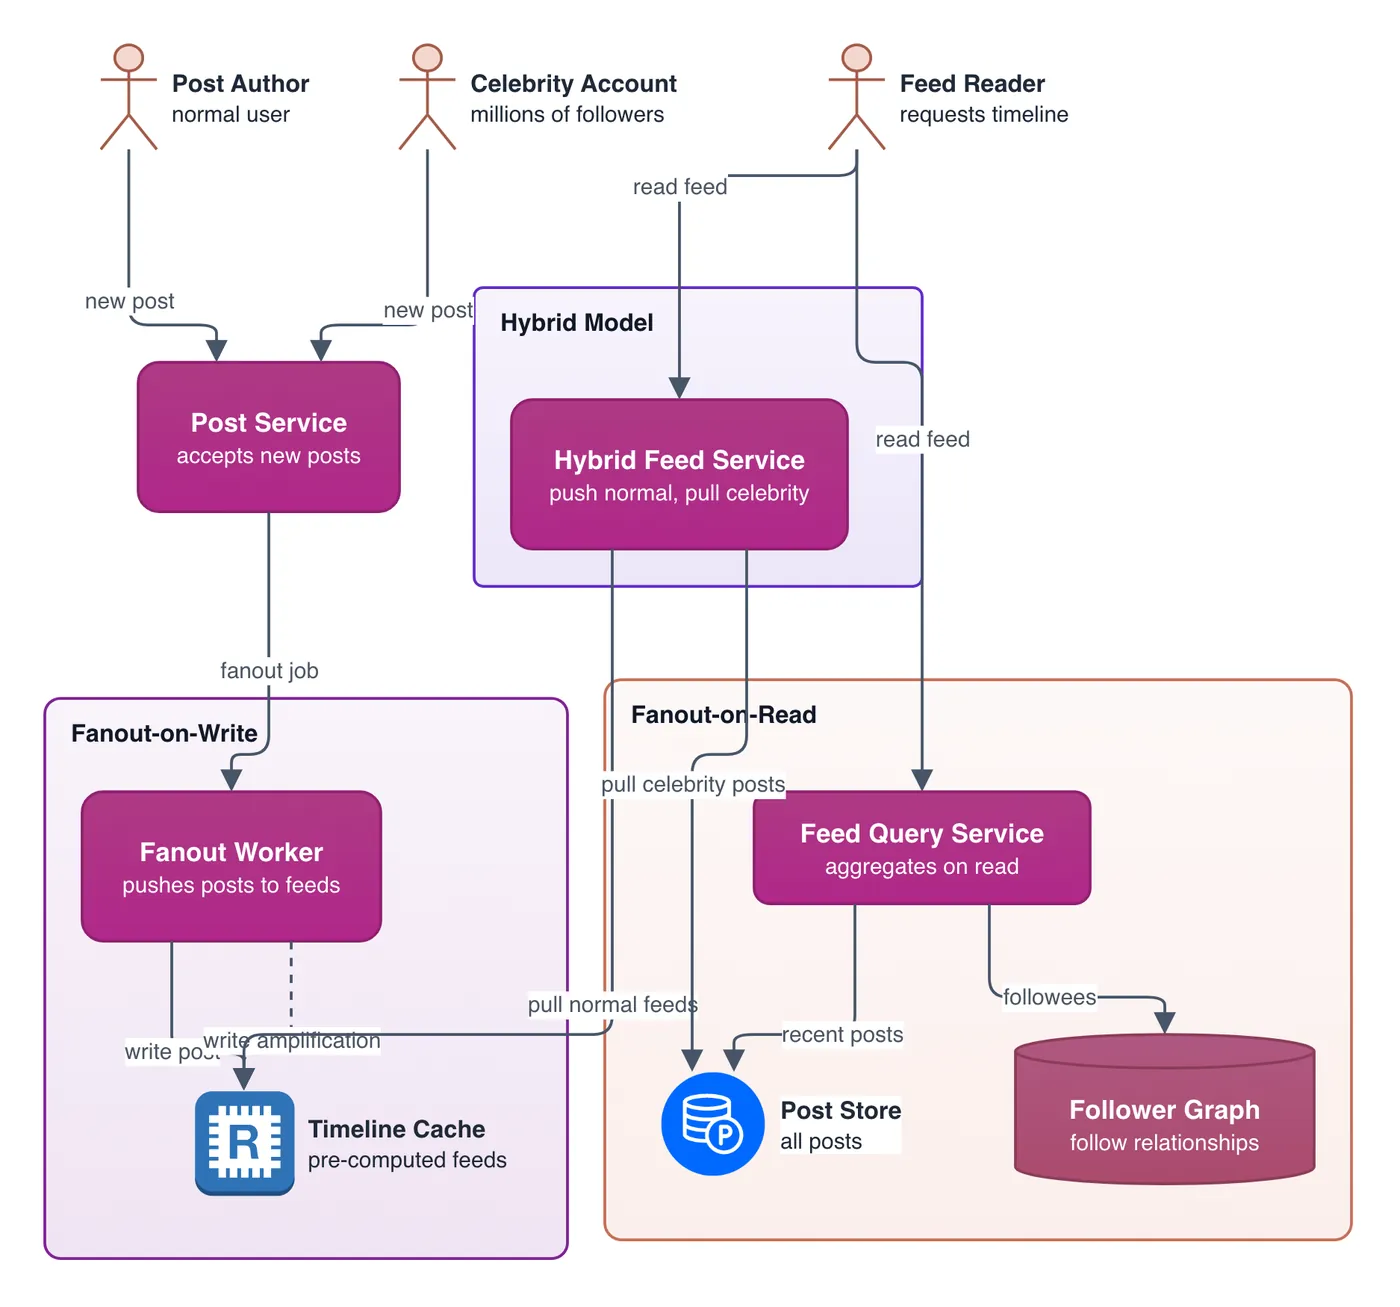
TOTP Authentication Architecture
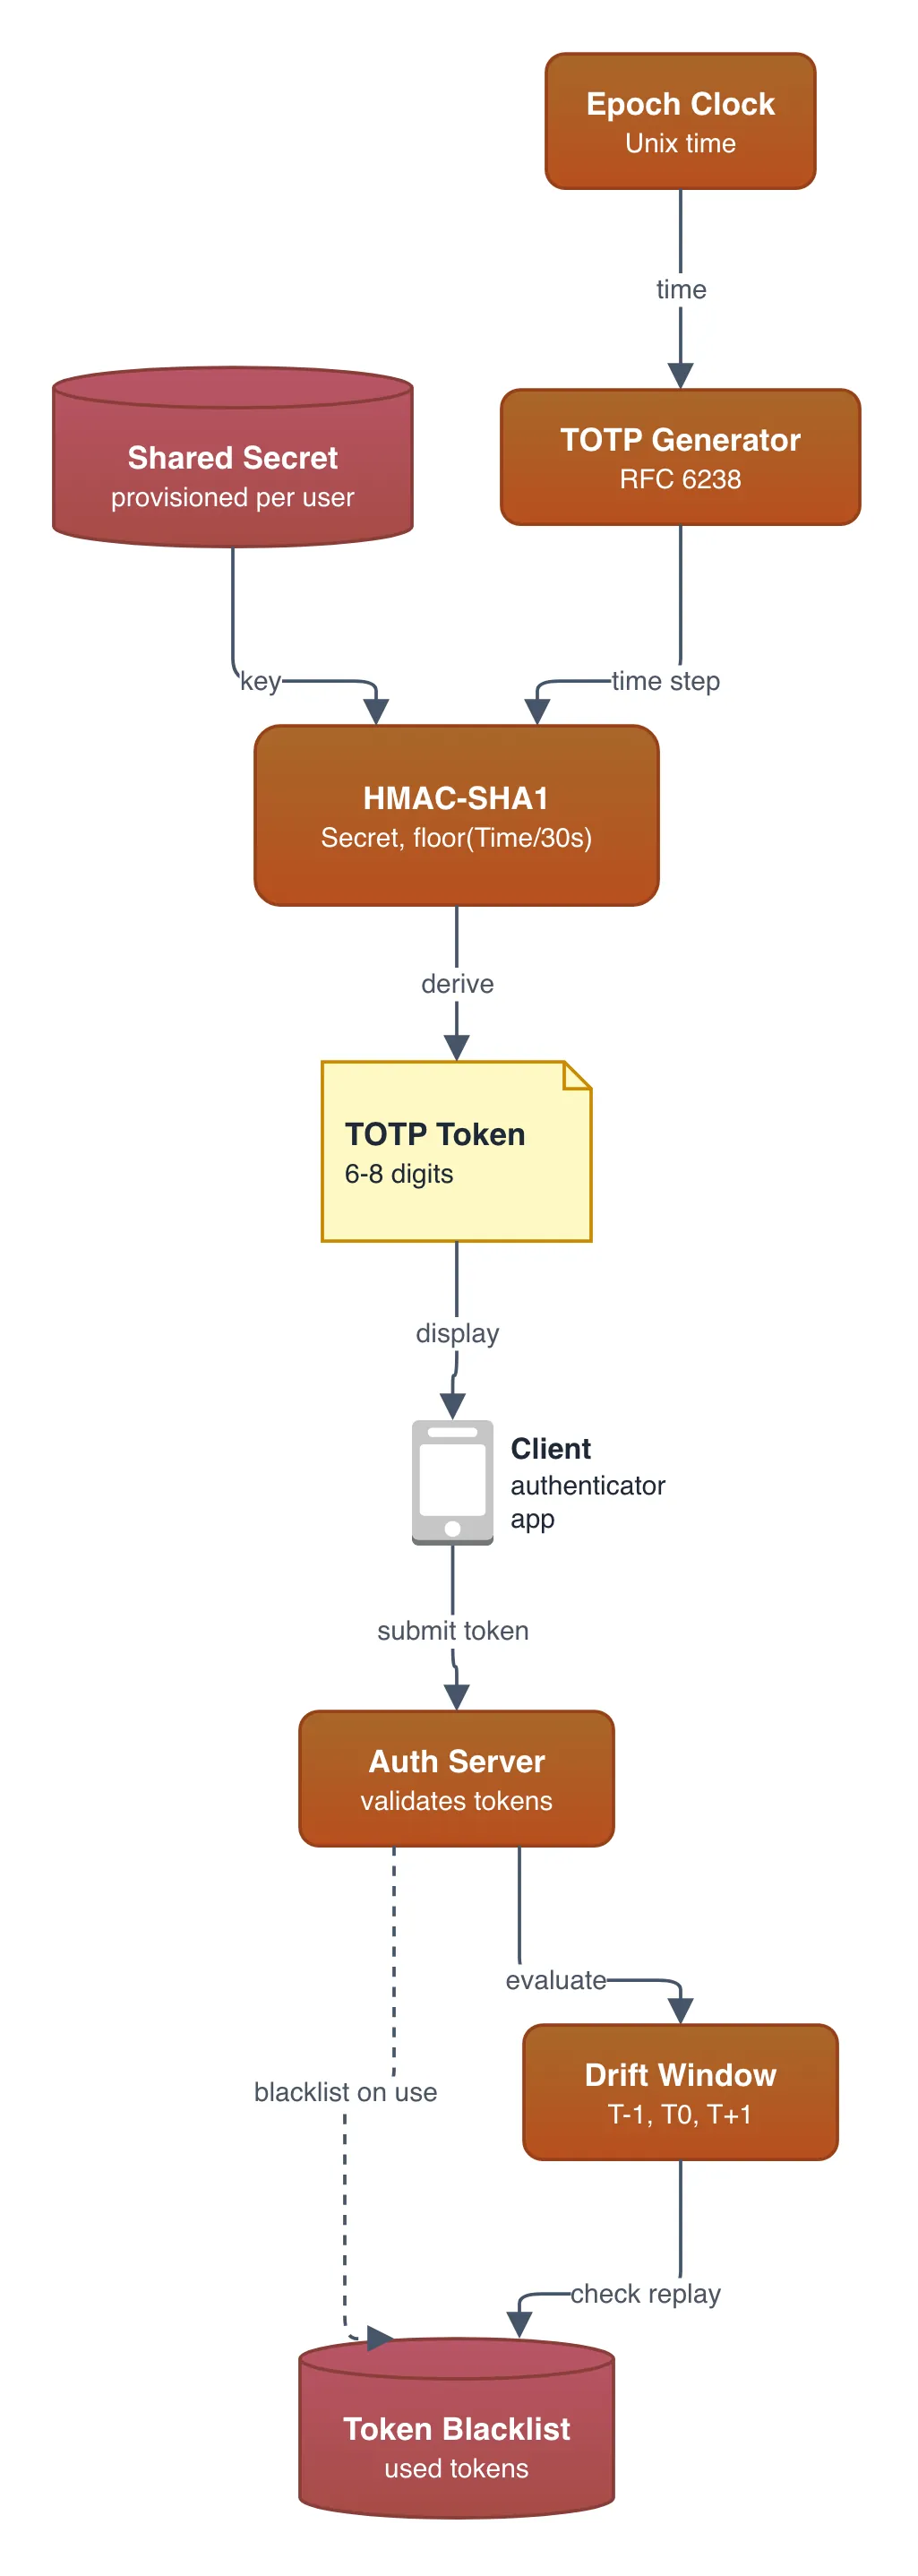
System Design diagram · made in Skemio
What it shows
- RFC 6238 derives tokens from HMAC-SHA1(Secret, Floor(Time / 30s))
- Servers evaluate T-1, T0, and T+1 steps to absorb client clock drift
- Tokens get blacklisted on use to stop replay attacks within windows
The takeaway
TOTP is stateless math: shared symmetric secrets paired with synchronized epoch time counters.
- #CyberSecurity
- #Authentication
- #SystemDesign
- #InfoSec
- #SoftwareEngineering
- #Backend