Zero-Egress Kubernetes Pod Network Policy
DevOps & CI/CD diagram · made in Skemio
What it shows
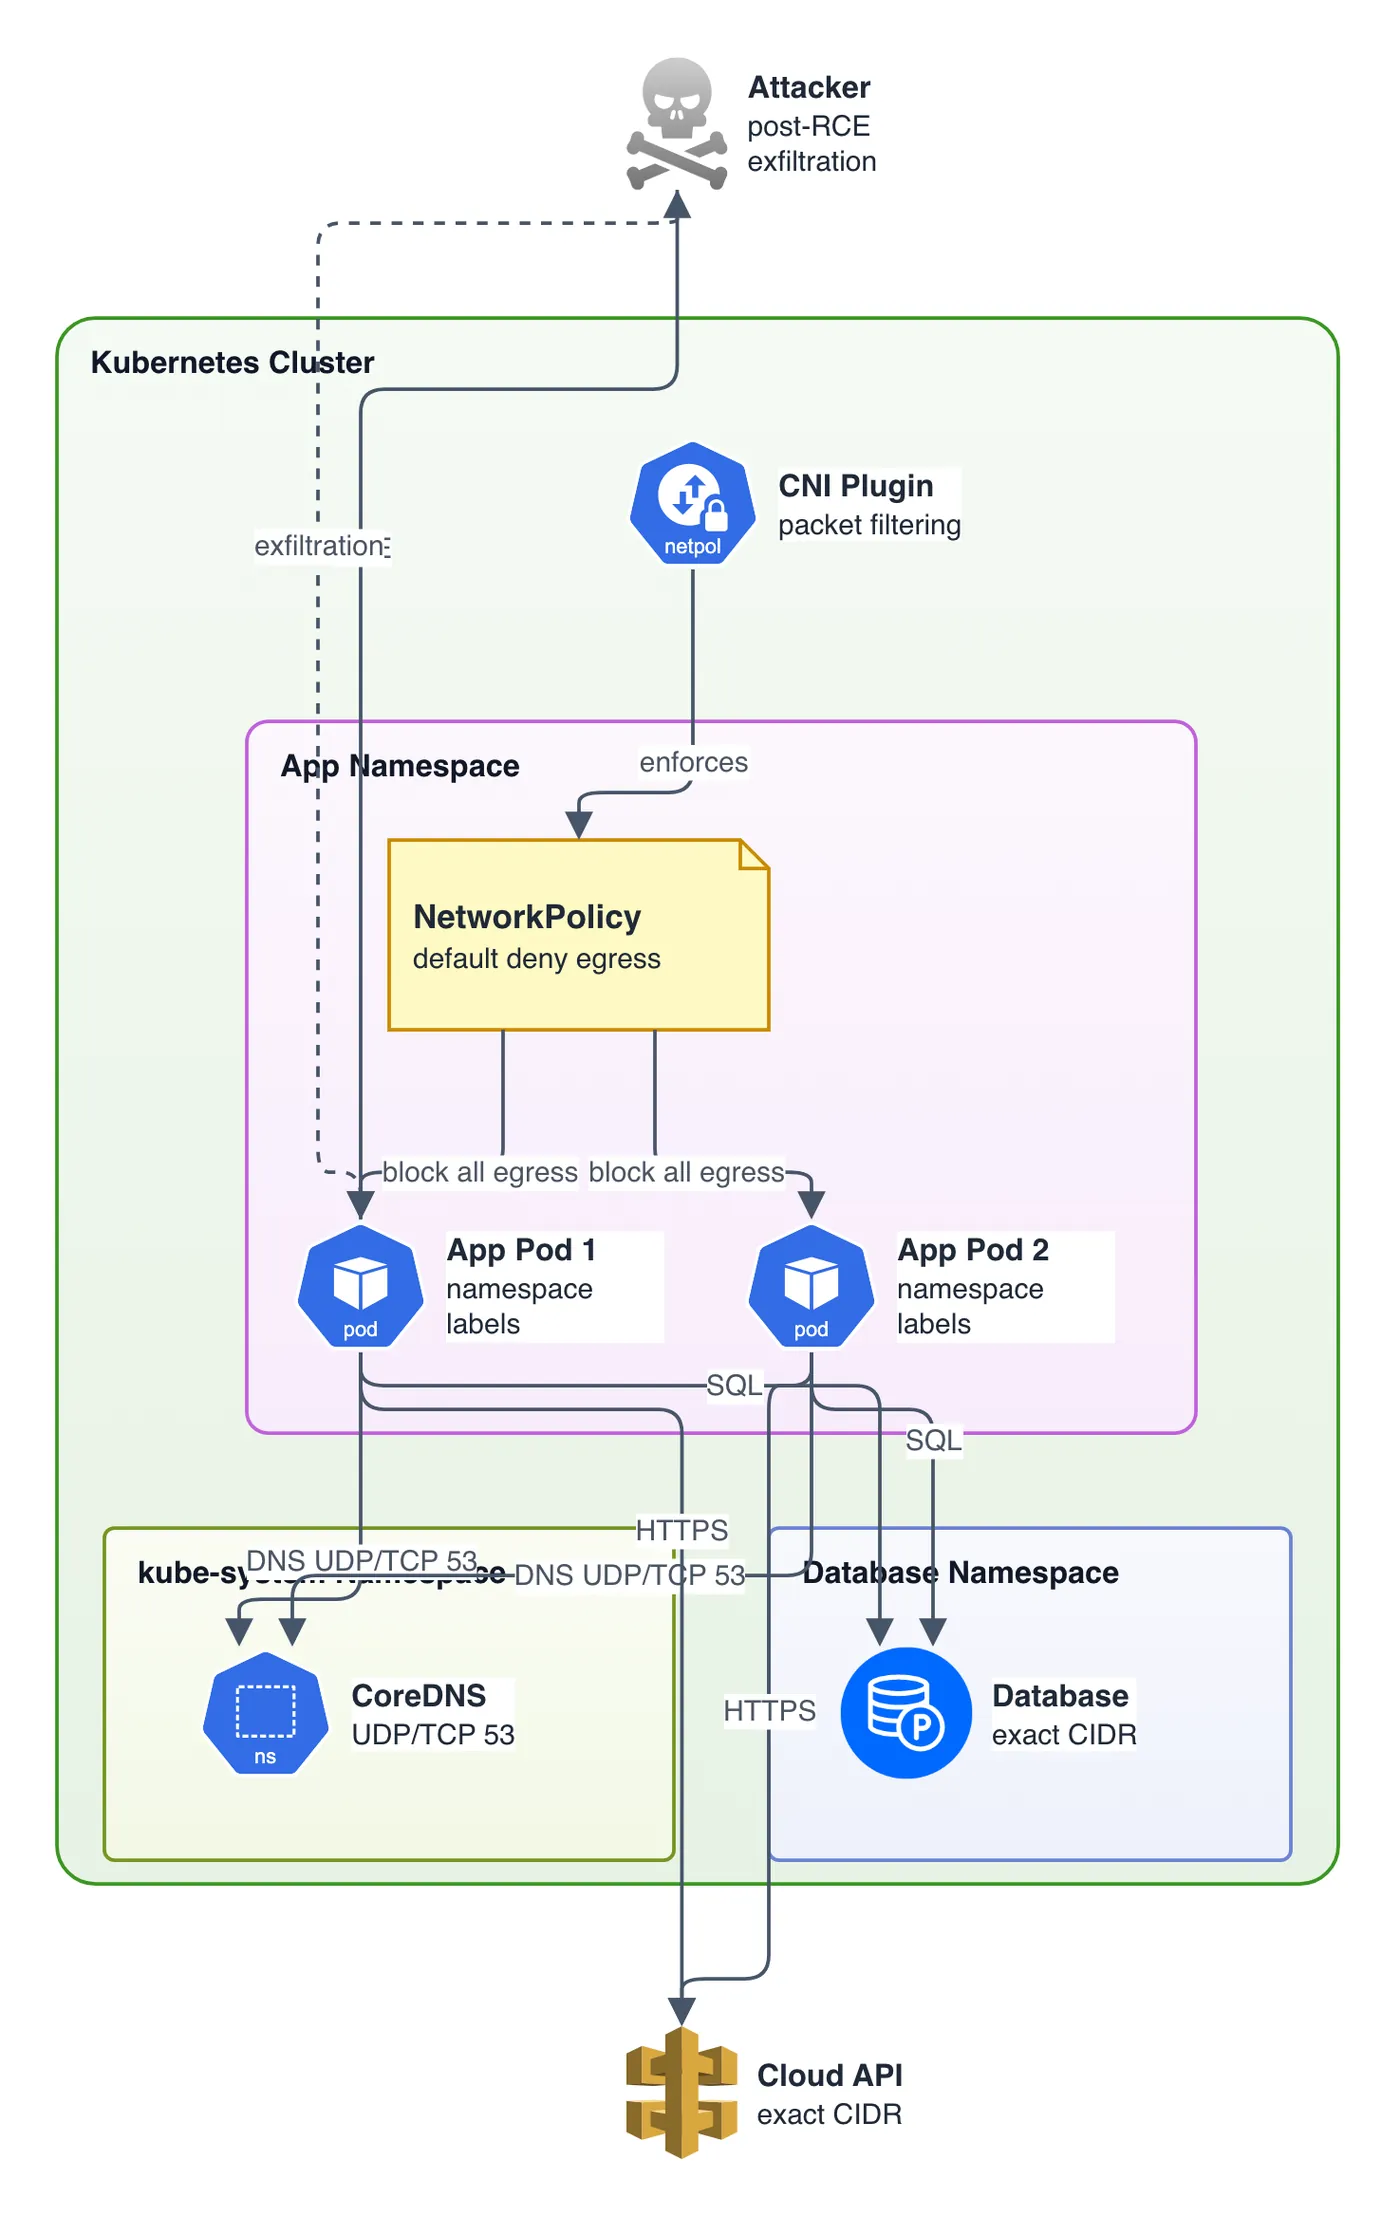
- Default-allow networking enables attackers to exfiltrate data after RCE
- Block all egress first; explicitly permit internal CoreDNS on UDP/TCP port 53
- Whitelist database and cloud API endpoints by exact CIDR and namespace labels
The takeaway
Enforce default-deny egress policies per namespace to contain compromised containers instantly.
- #Kubernetes
- #DevOps
- #CloudSecurity
- #DevSecOps
- #ContainerSecurity
- #Networking