Zero-Trust Secret Injection with HashiCorp Vault
DevOps & CI/CD diagram · made in Skemio
What it shows
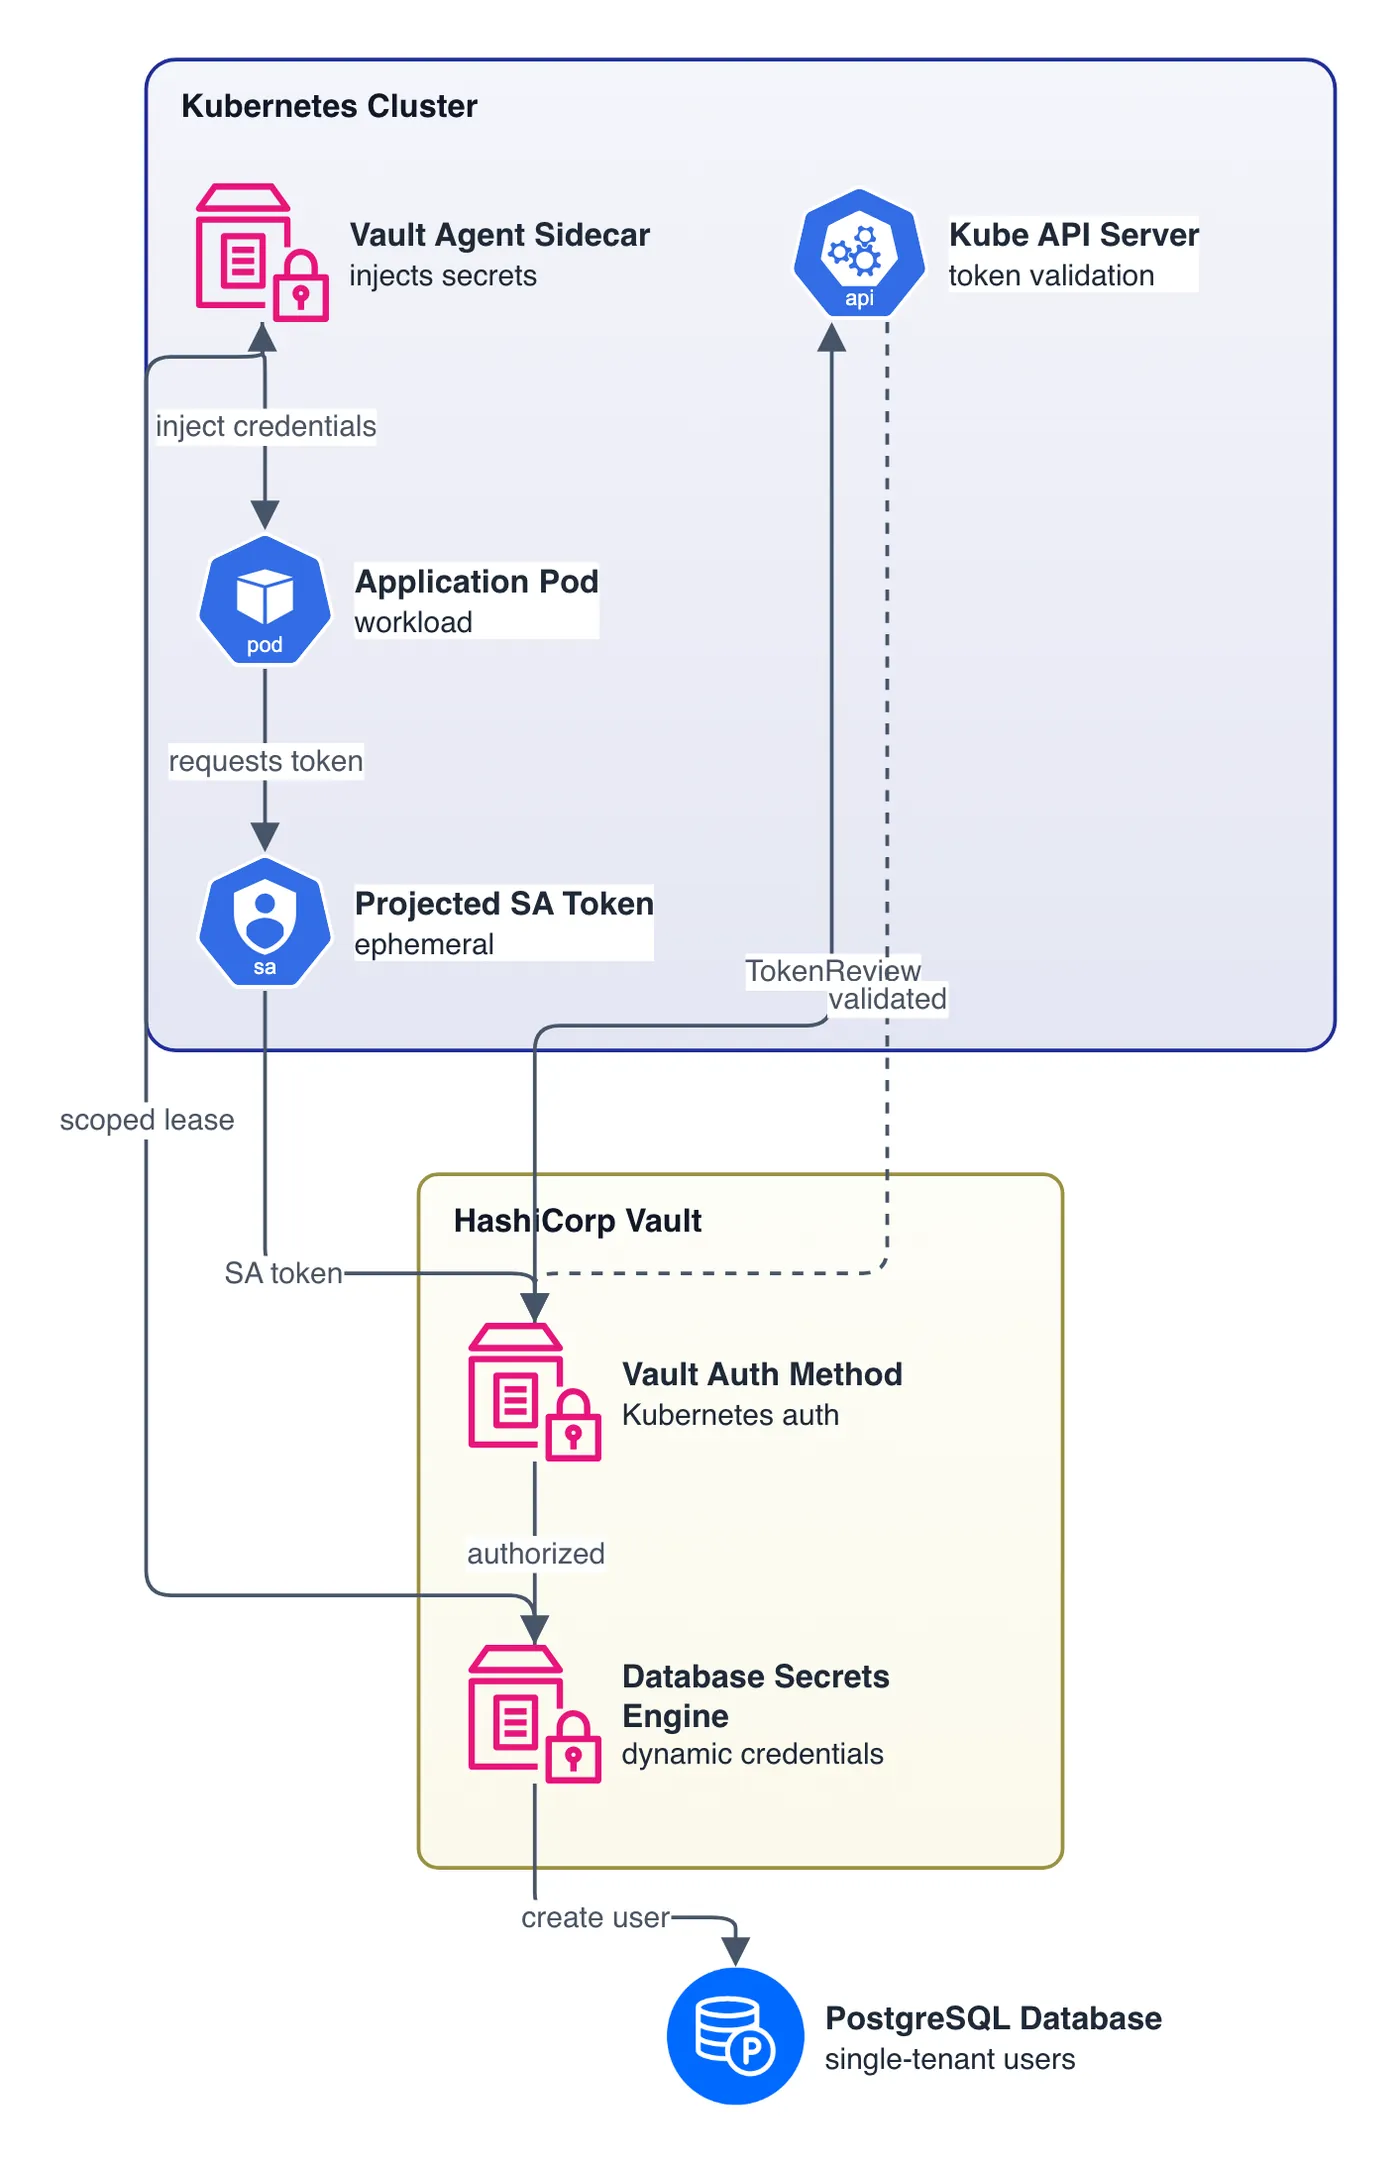
- Kubernetes pods authenticate to Vault using ephemeral projected service account tokens.
- Vault validates tokens via the Kube API server before returning scoped client leases.
- Dynamic engine generates single-tenant DB users that expire automatically in hours.
The takeaway
Replace static secrets with identity-based token exchange and dynamic credential generation.
- #Kubernetes
- #Vault
- #ZeroTrust
- #DevOps
- #CloudSecurity