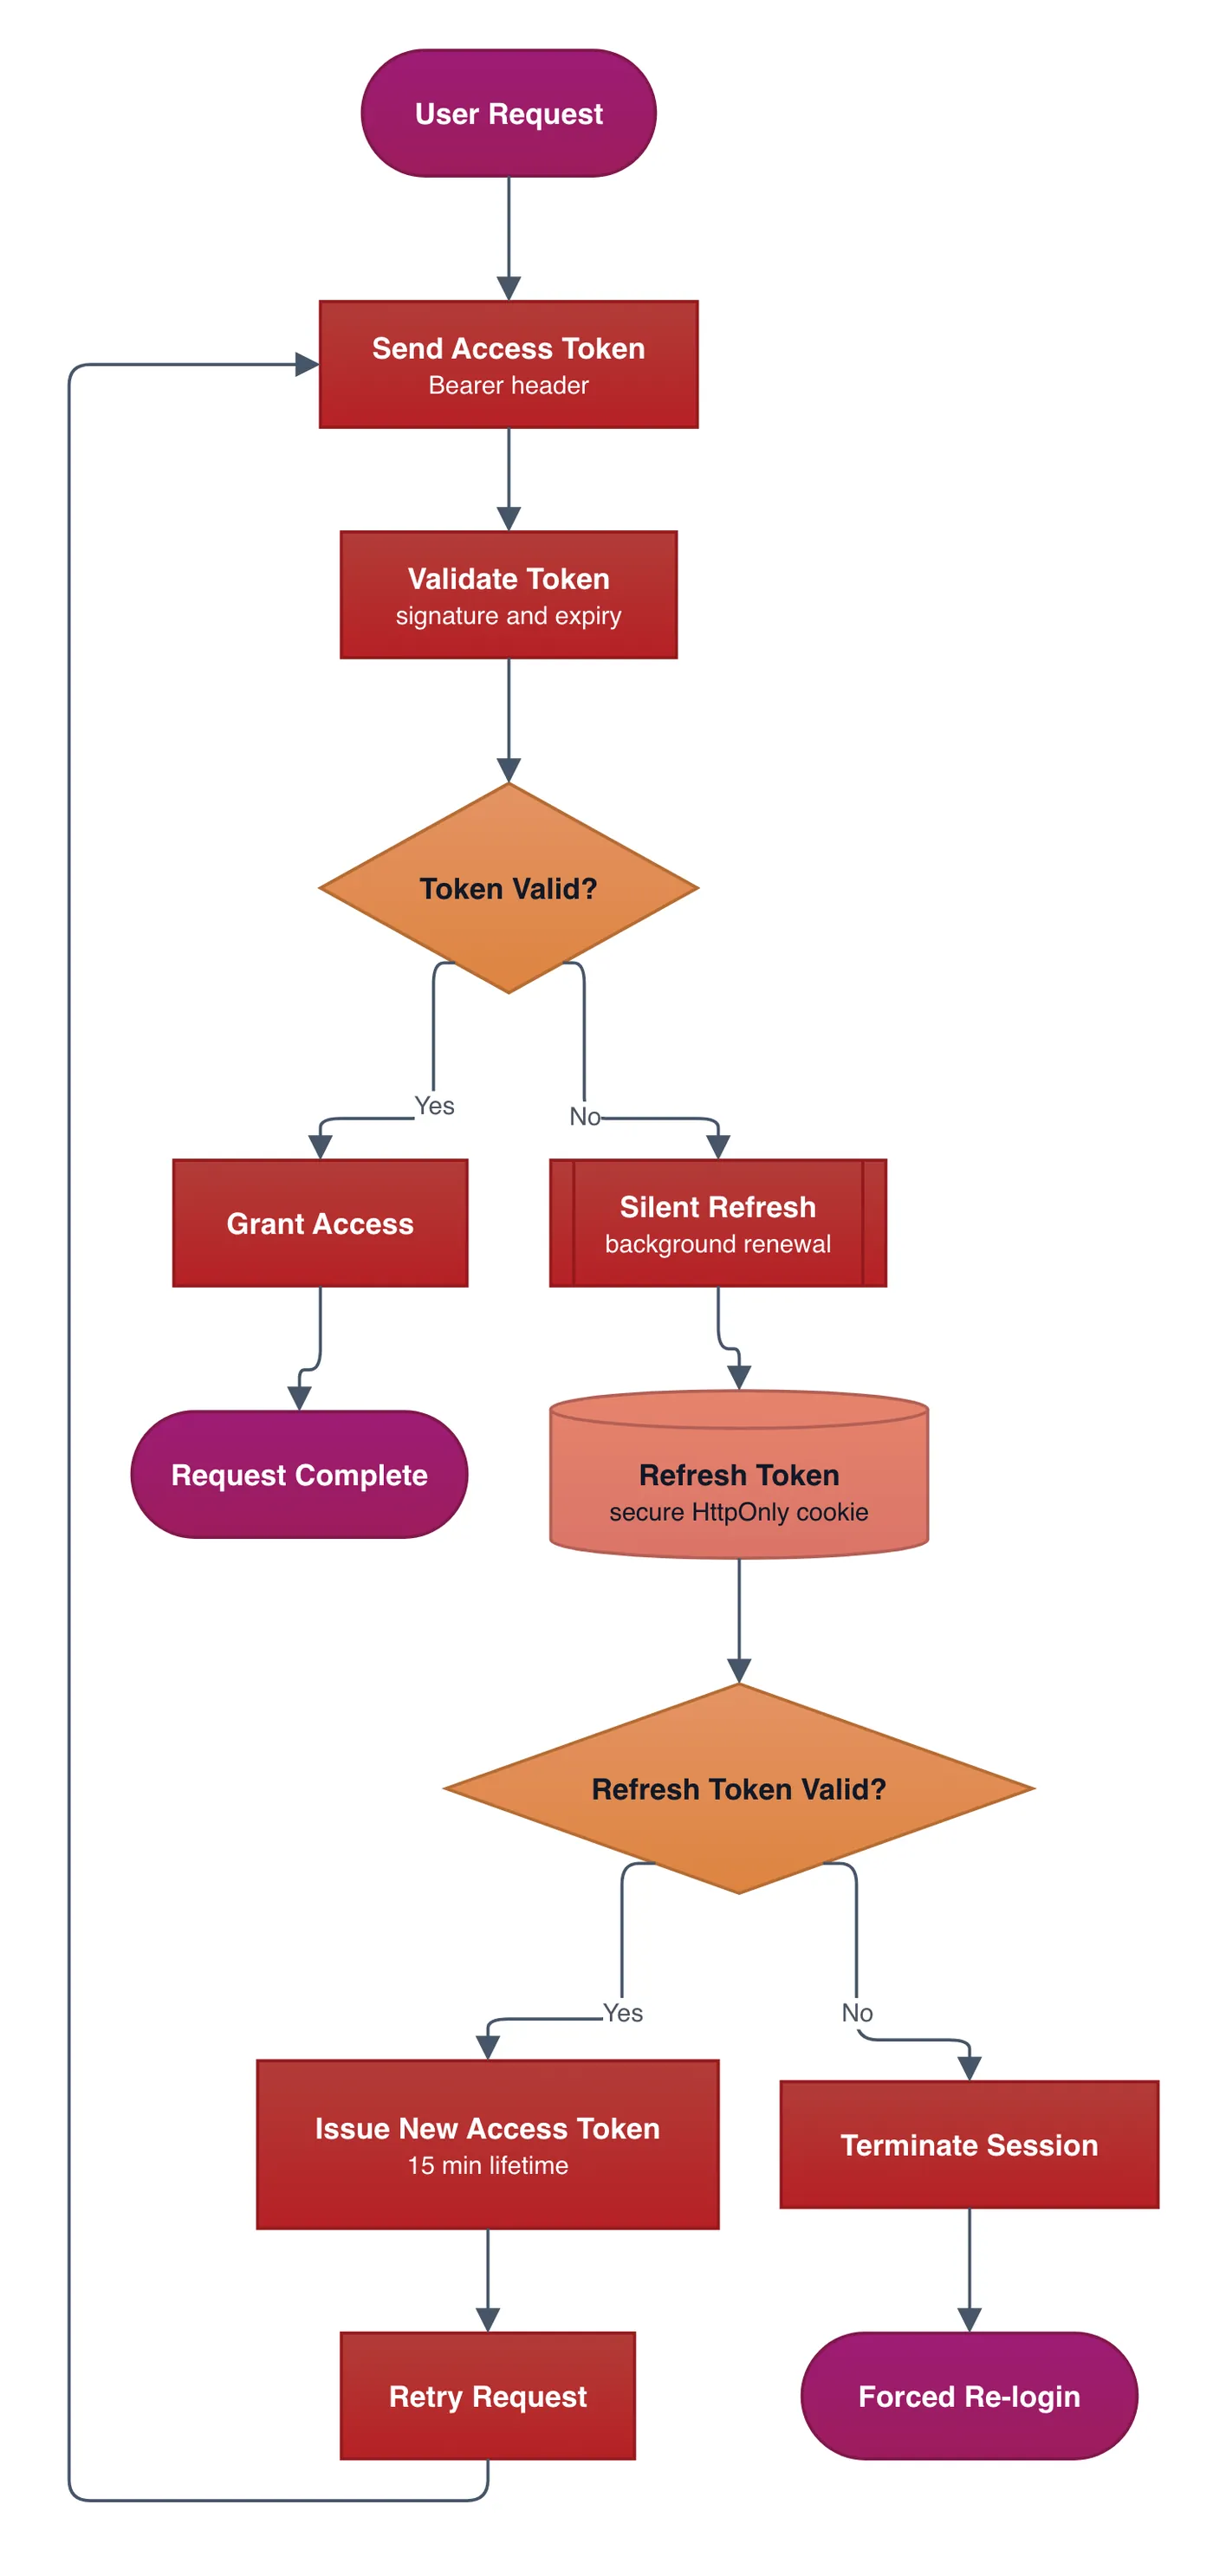
JWT Authentication and Refresh Flow
Flowcharts & Algorithms diagram · made in Skemio
What it shows
- Short-lived access tokens (15 mins) minimize impact of token theft.
- Refresh tokens stored in secure HttpOnly cookies handle background renewals.
- Invalid or expired refresh tokens immediately terminate user sessions.
The takeaway
Pair short-lived access tokens with rotating refresh tokens for stateless speed and rapid revocation.
- #JWT
- #Authentication
- #WebSecurity
- #BackendDevelopment
- #SoftwareArchitecture
- #APIs