OAuth 2.0 PKCE: Securing Public Clients
UML Sequence Diagrams · made in Skemio
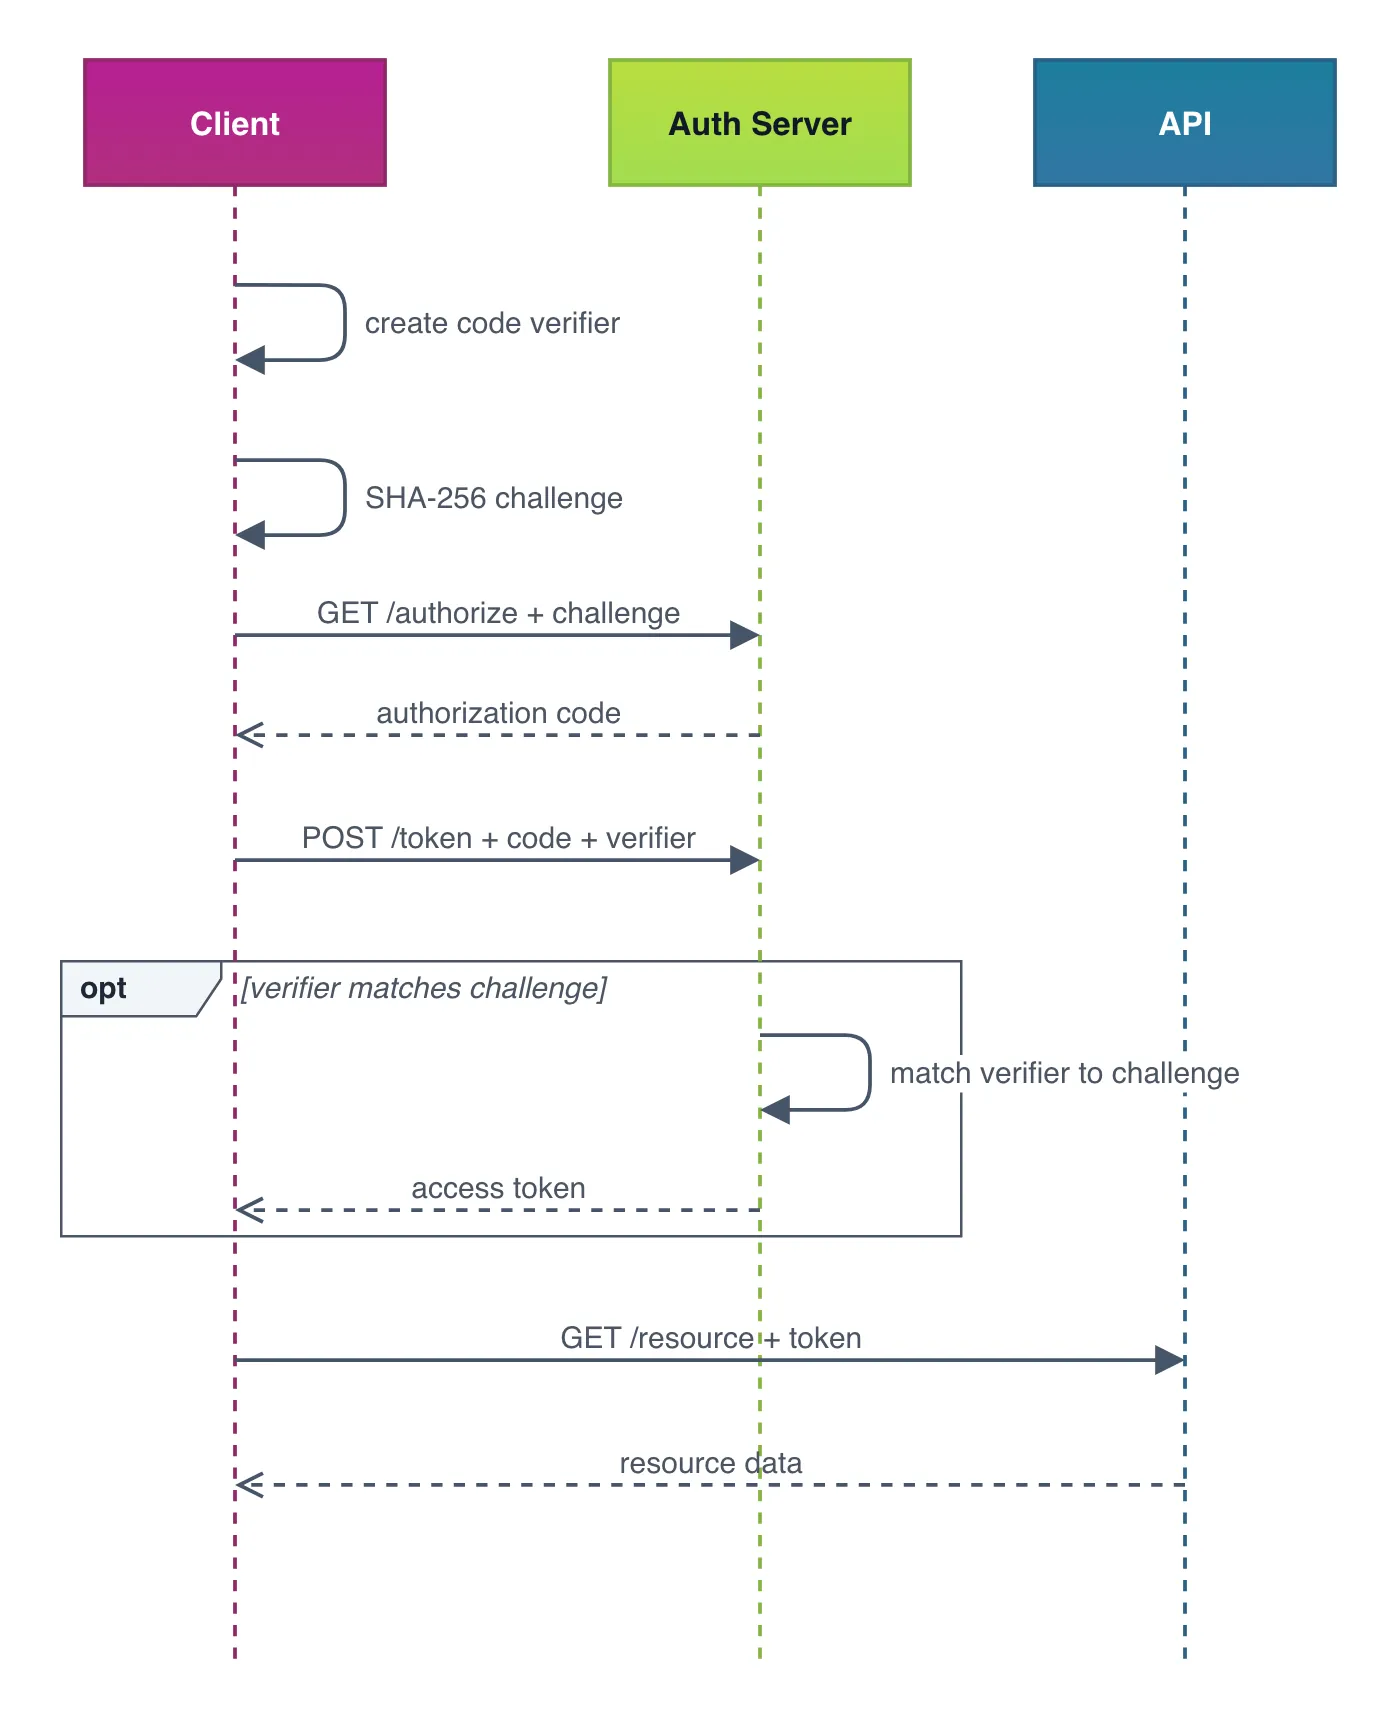
What it shows
- Client creates a cryptographic code verifier and SHA-256 challenge.
- Auth server matches verifier against challenge before issuing tokens.
- Neutralizes authorization code interception attacks on public devices.
The takeaway
PKCE eliminates static secrets on public clients by dynamically verifying the code requester.
- #OAuth2AppSecuritySystemDesignWebDevSoftwareEngineeringIdentity