OpenID Connect: Identity on Top of OAuth
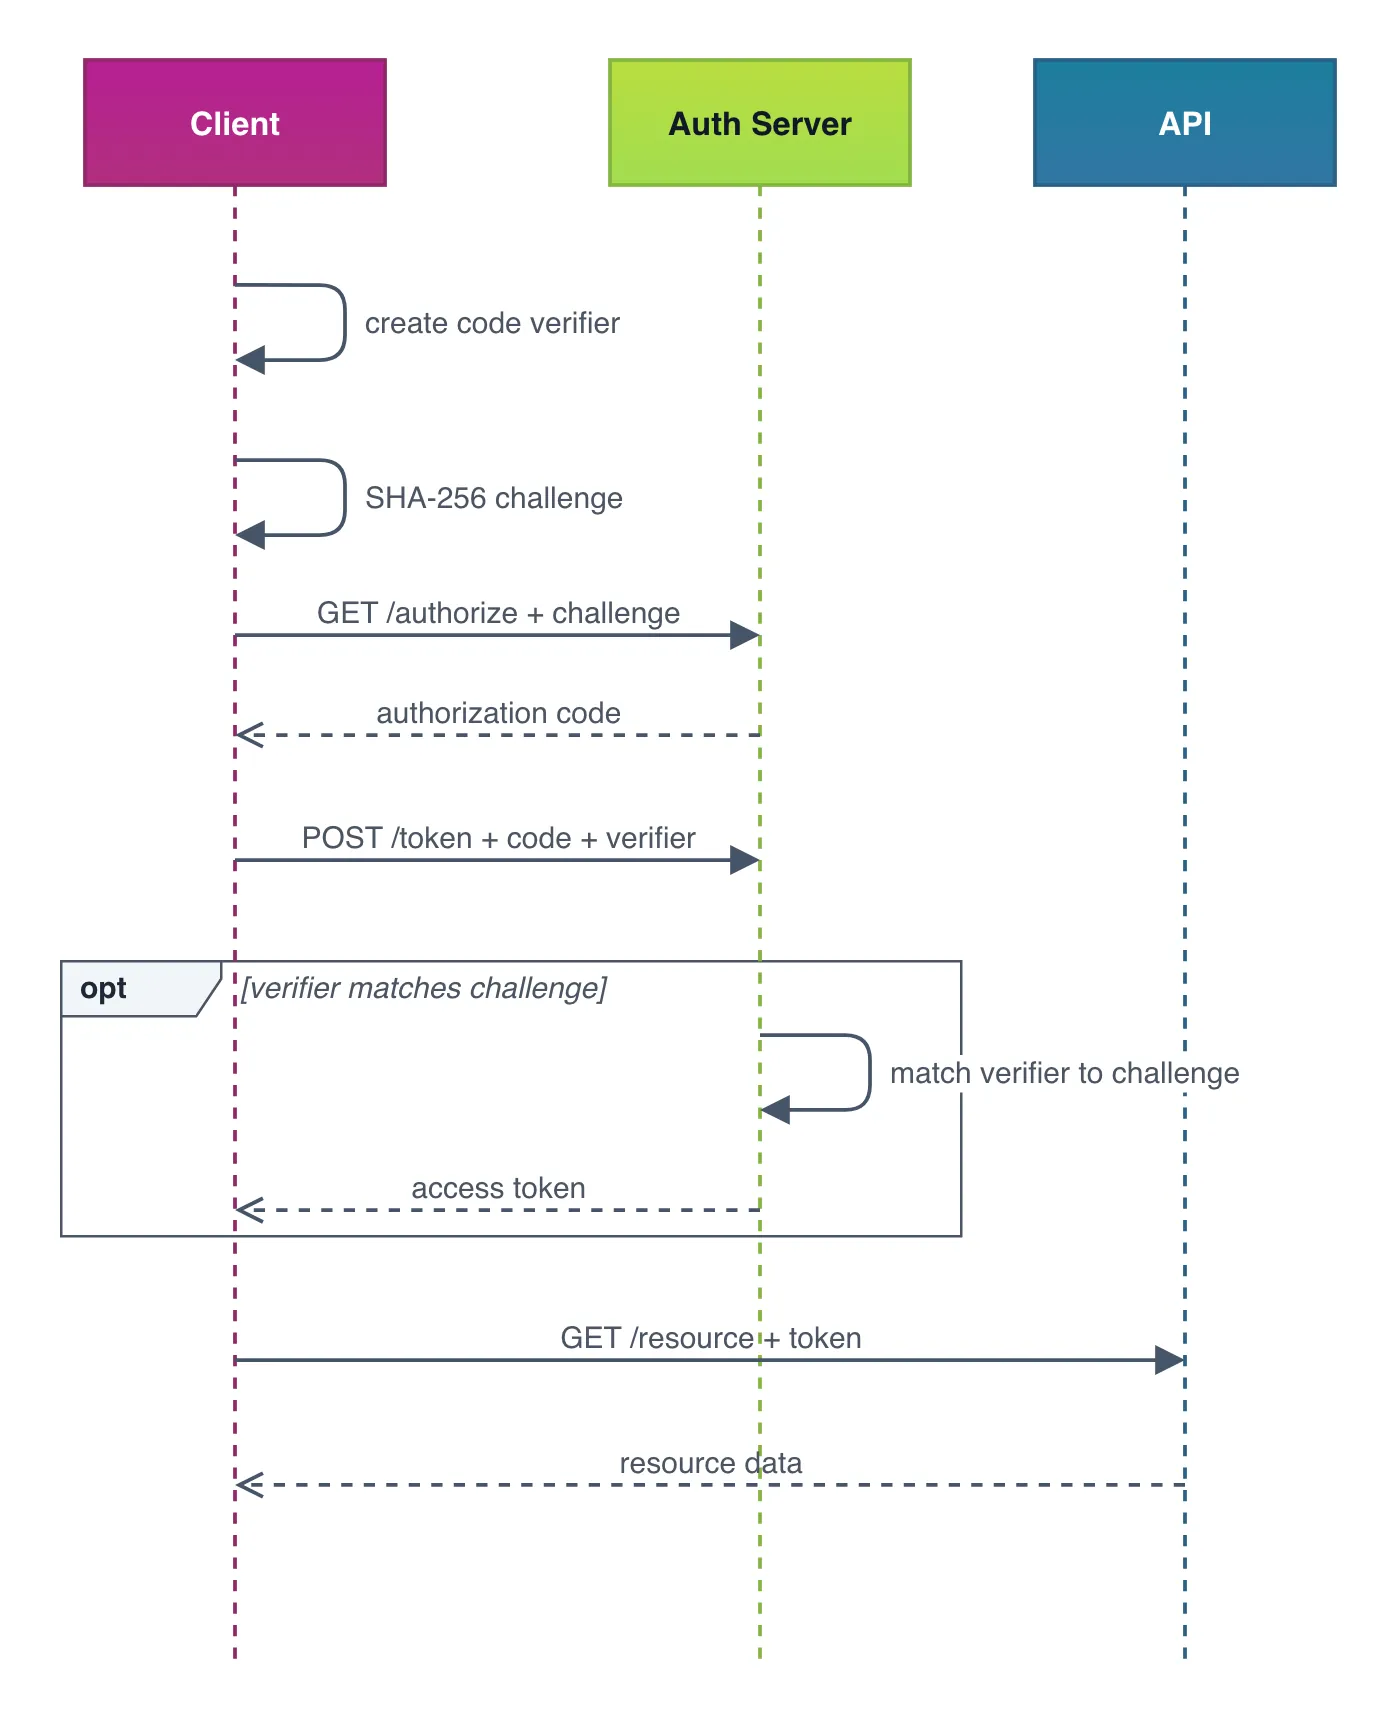
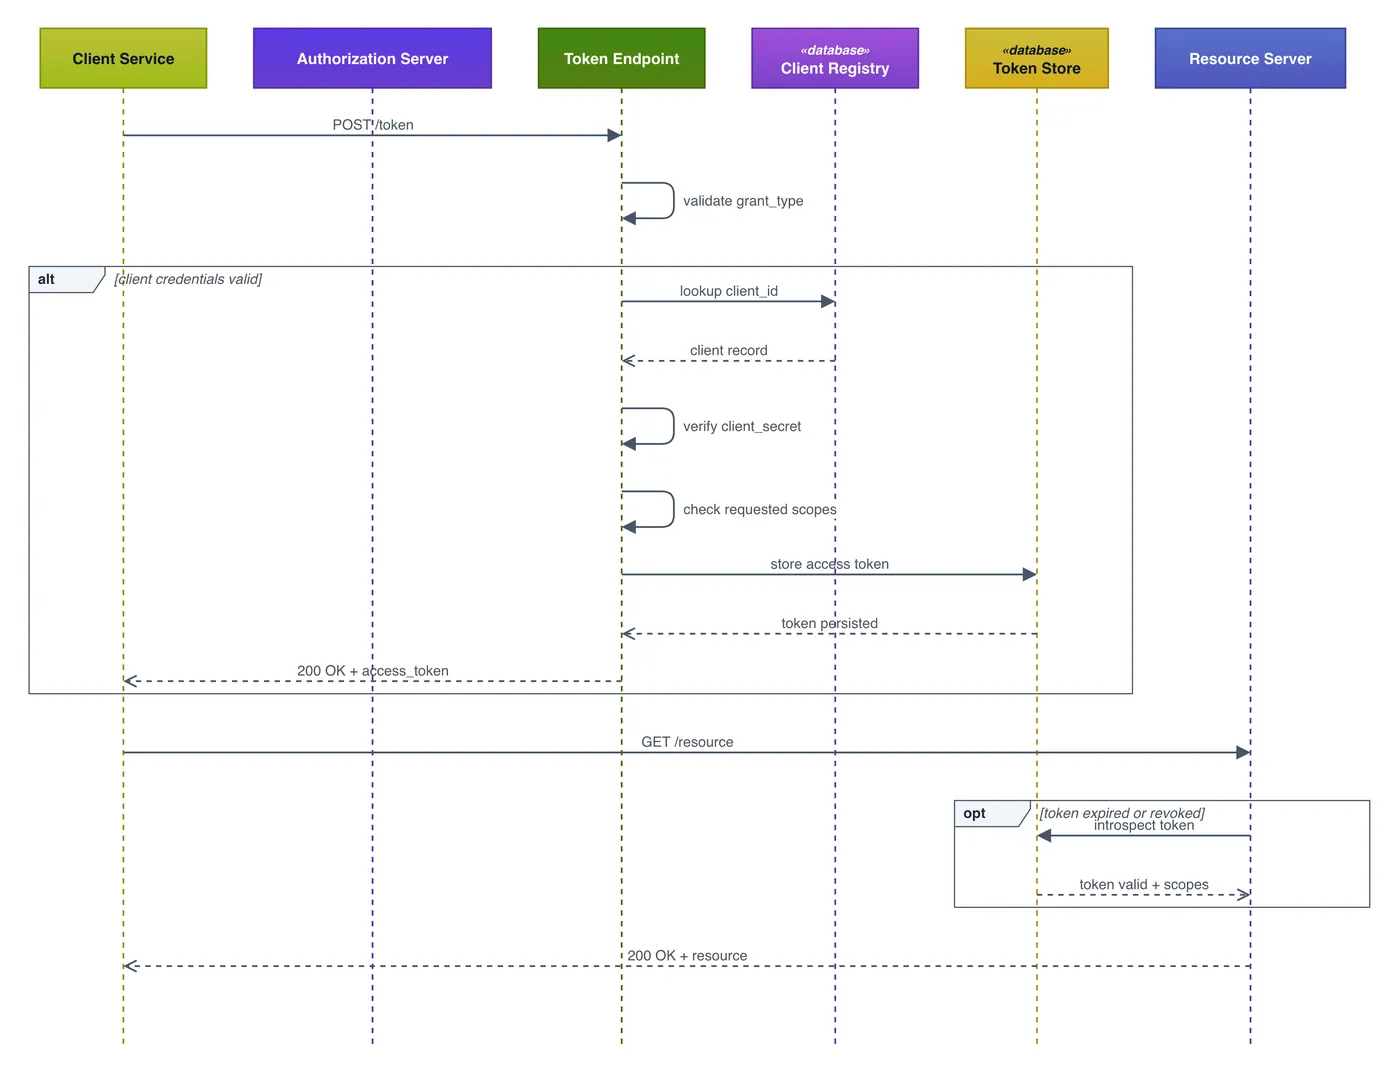
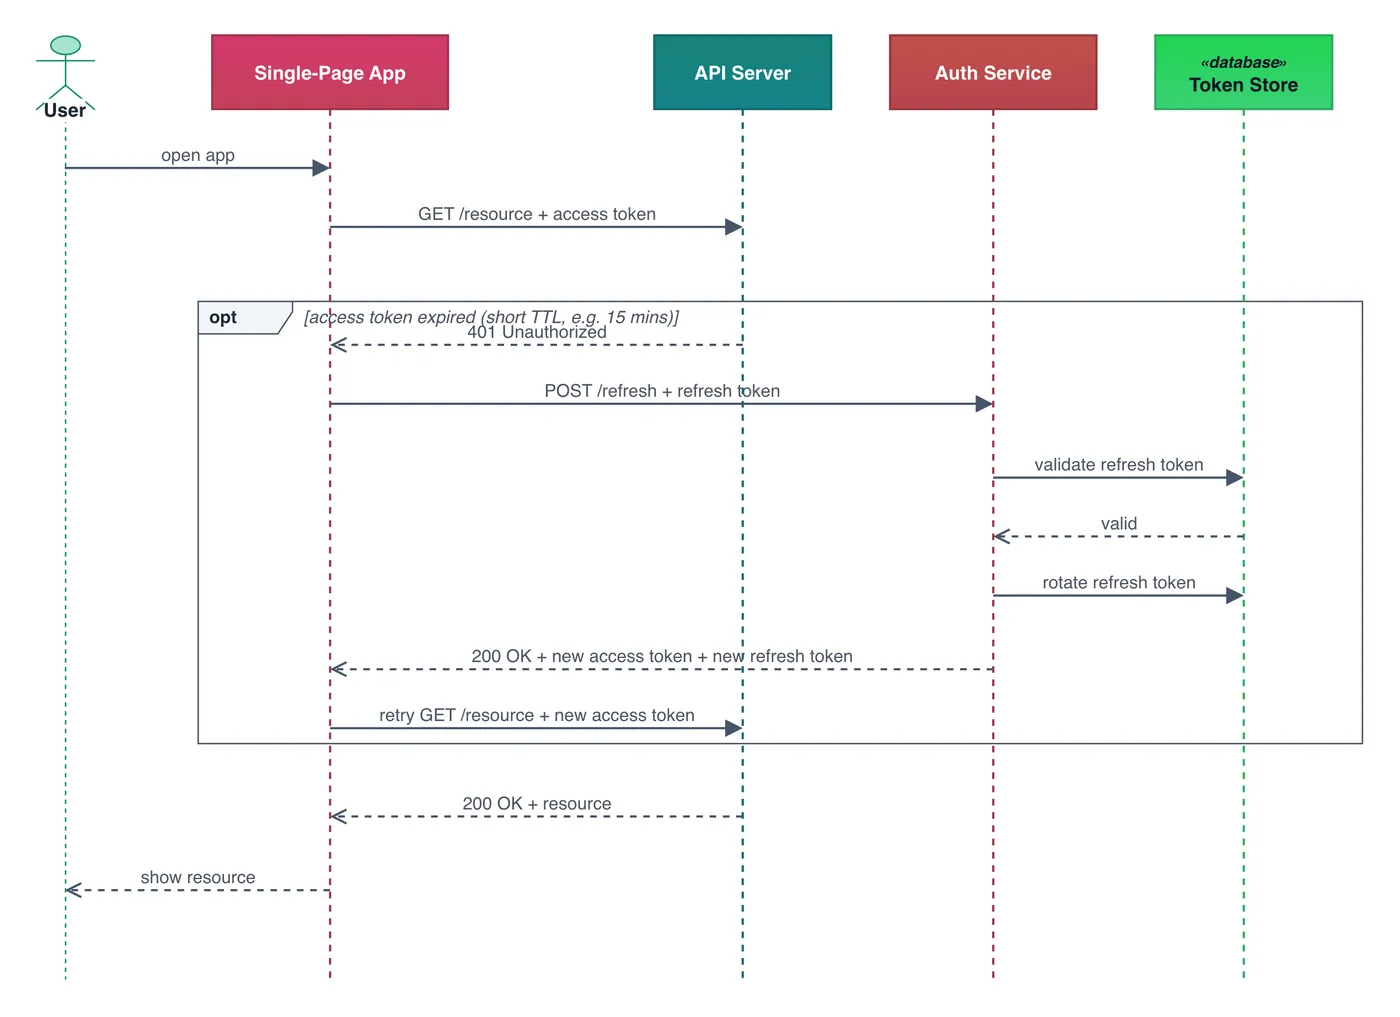
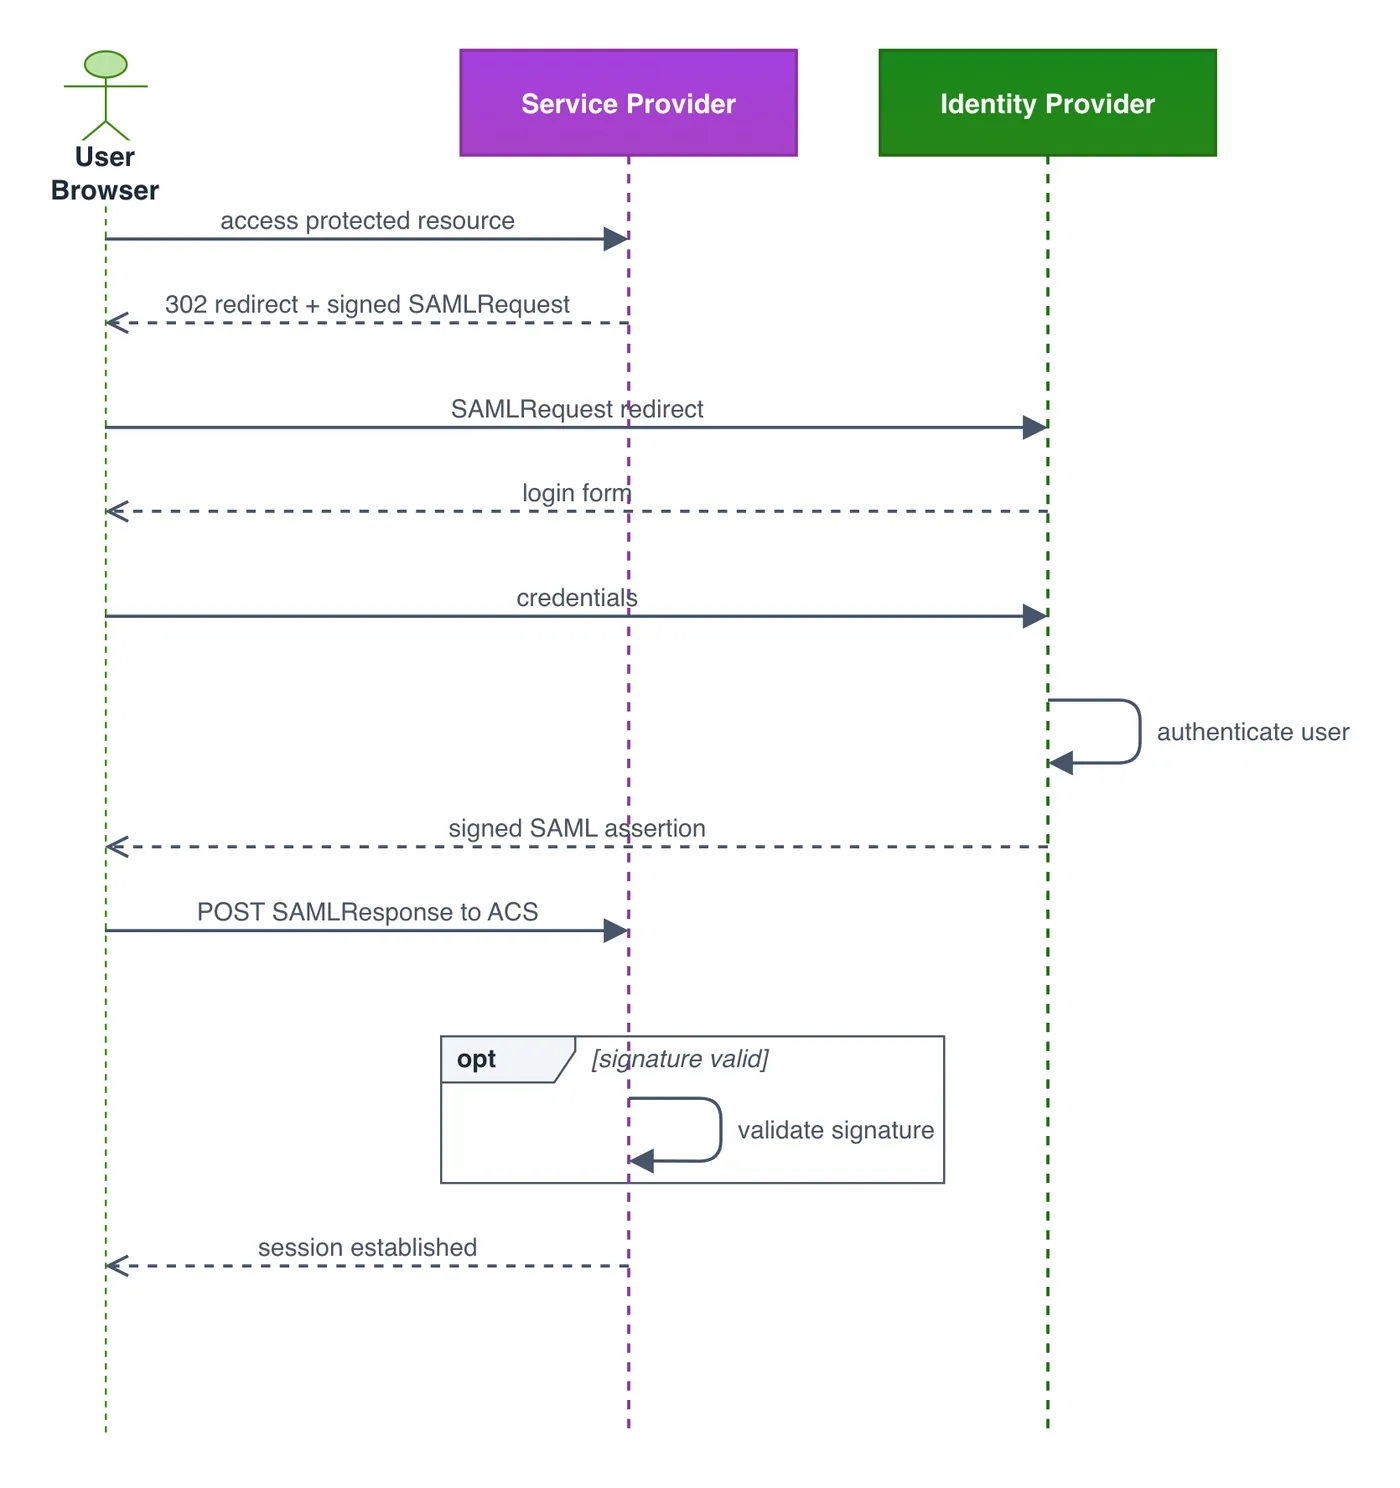
UML Sequence Diagrams · made in Skemio
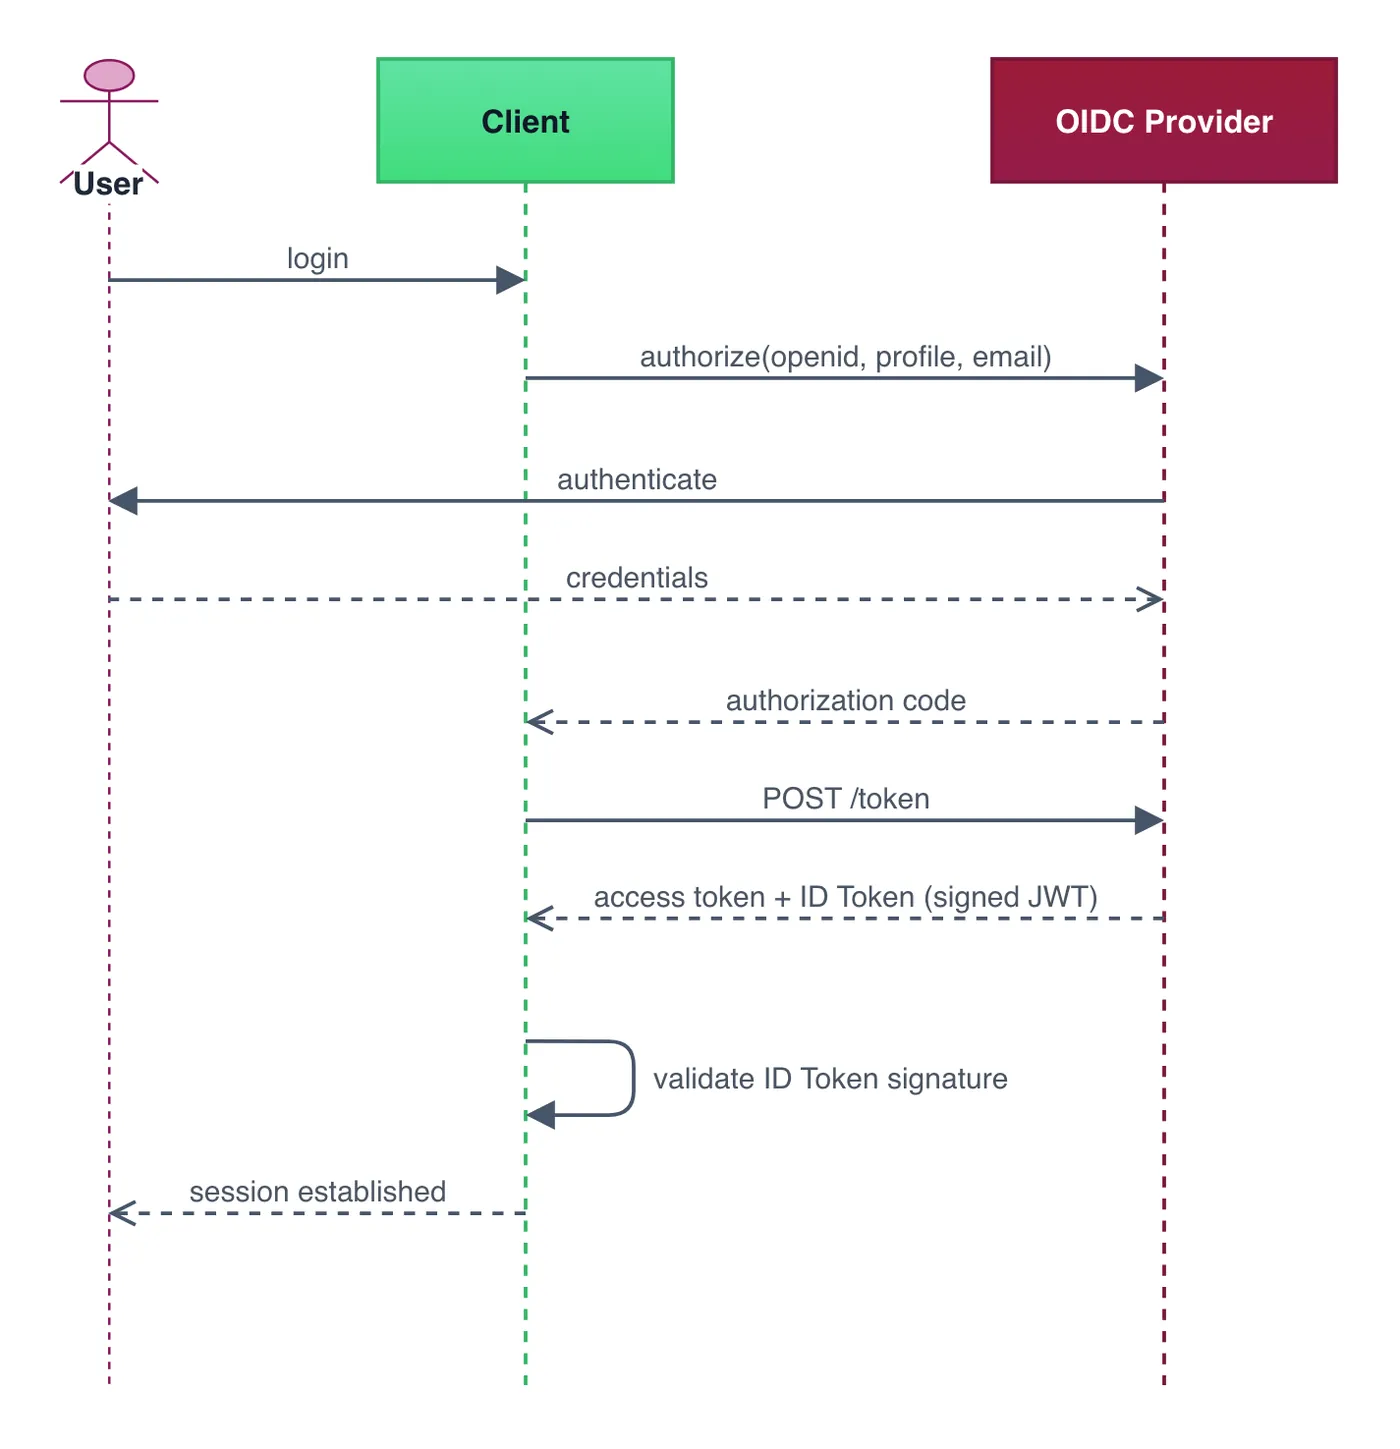
What it shows
- OIDC introduces the ID Token, a signed JWT containing user profile claims.
- Standardizes scopes like 'openid', 'profile', and 'email' across providers.
- Clients verify identity locally by validating the ID Token signature.
The takeaway
OAuth grants access to resources; OpenID Connect tells your application who the authenticated user is.
- #OIDCIdentityAuthenticationOAuth2SecurityWebDev