SAML 2.0 SSO: Enterprise Identity Exchange
UML Sequence Diagrams · made in Skemio
What it shows
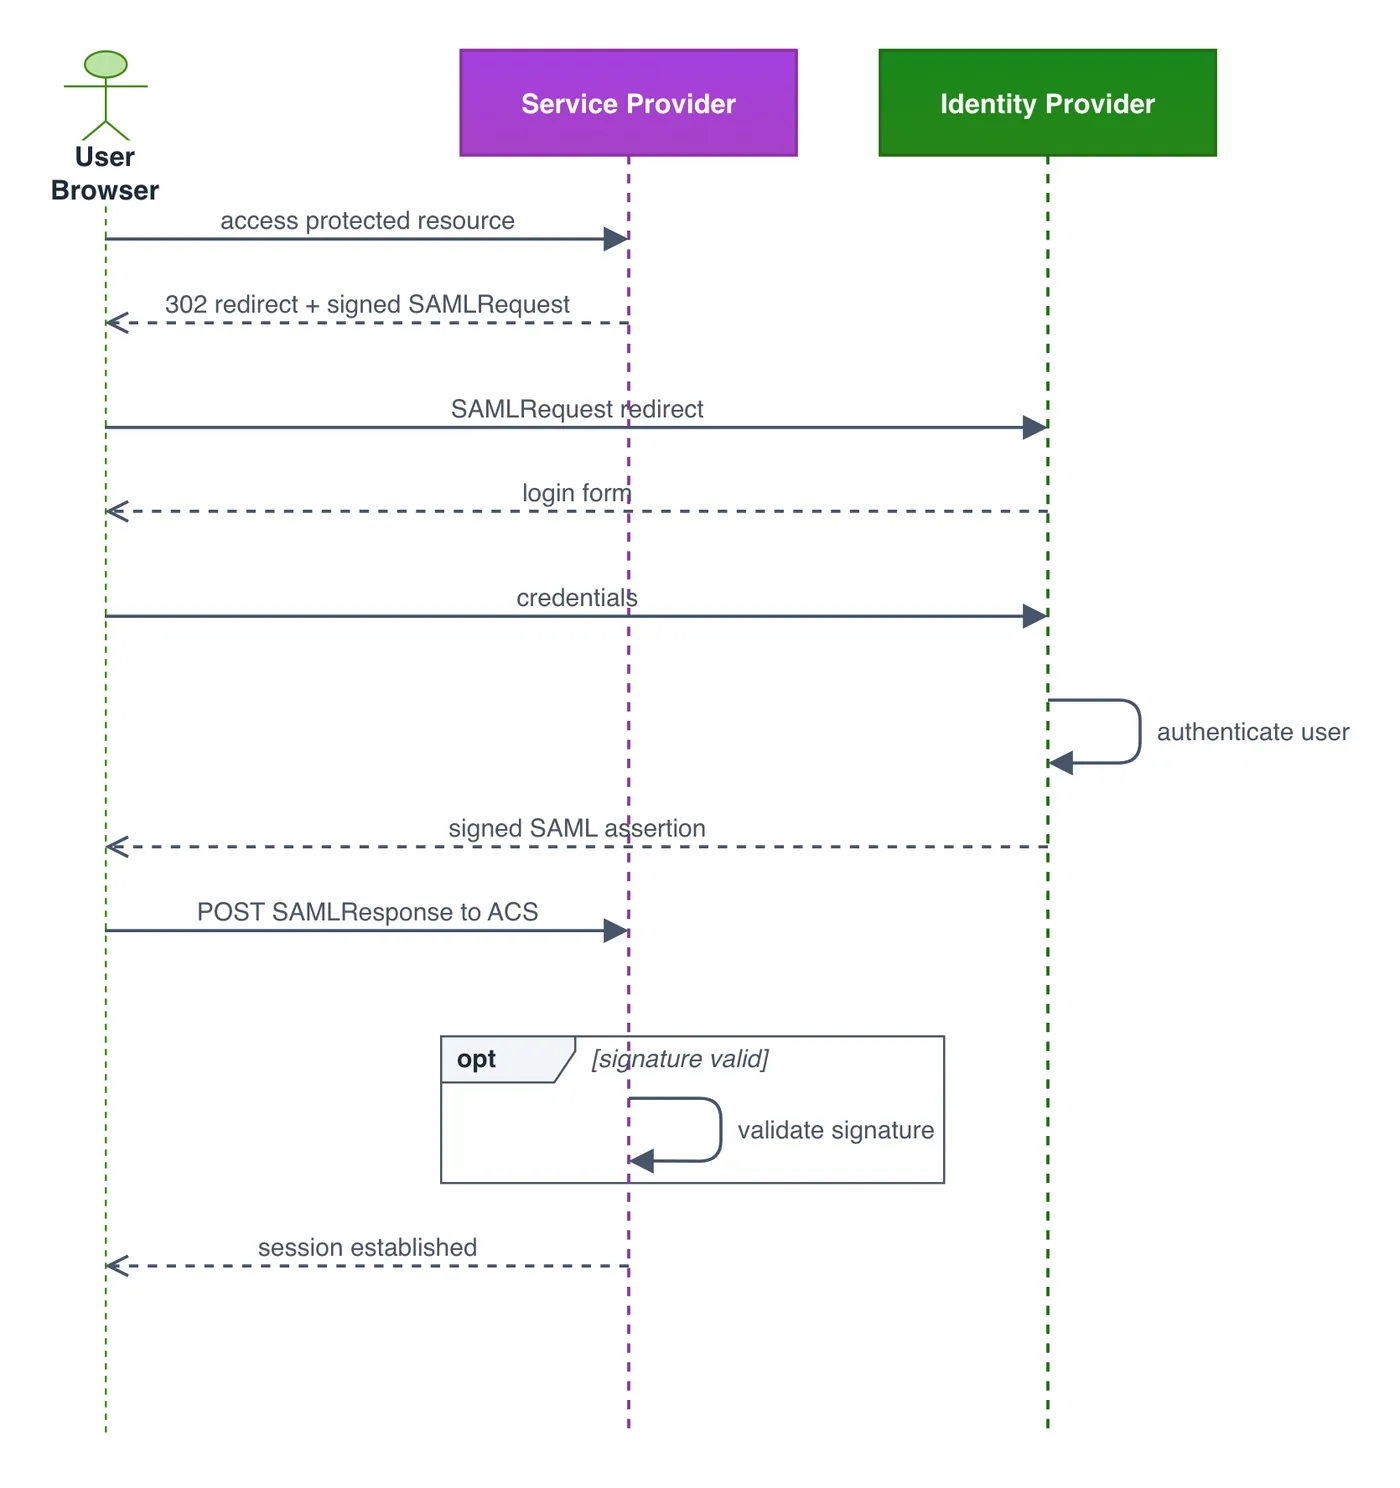
- Service Provider initiates login with a signed SAMLRequest redirect.
- Identity Provider issues digitally signed XML assertions via user browser.
- ACS validates signatures without direct backend SP-to-IdP connections.
The takeaway
SAML 2.0 delegates authentication to an enterprise IdP via signed XML assertions routed through the browser.
- #SAML2SingleSignOnSSOEnterpriseITCyberSecurityIdentity