Secure Webhook Verification via HMAC Signatures
UML Sequence Diagrams · made in Skemio
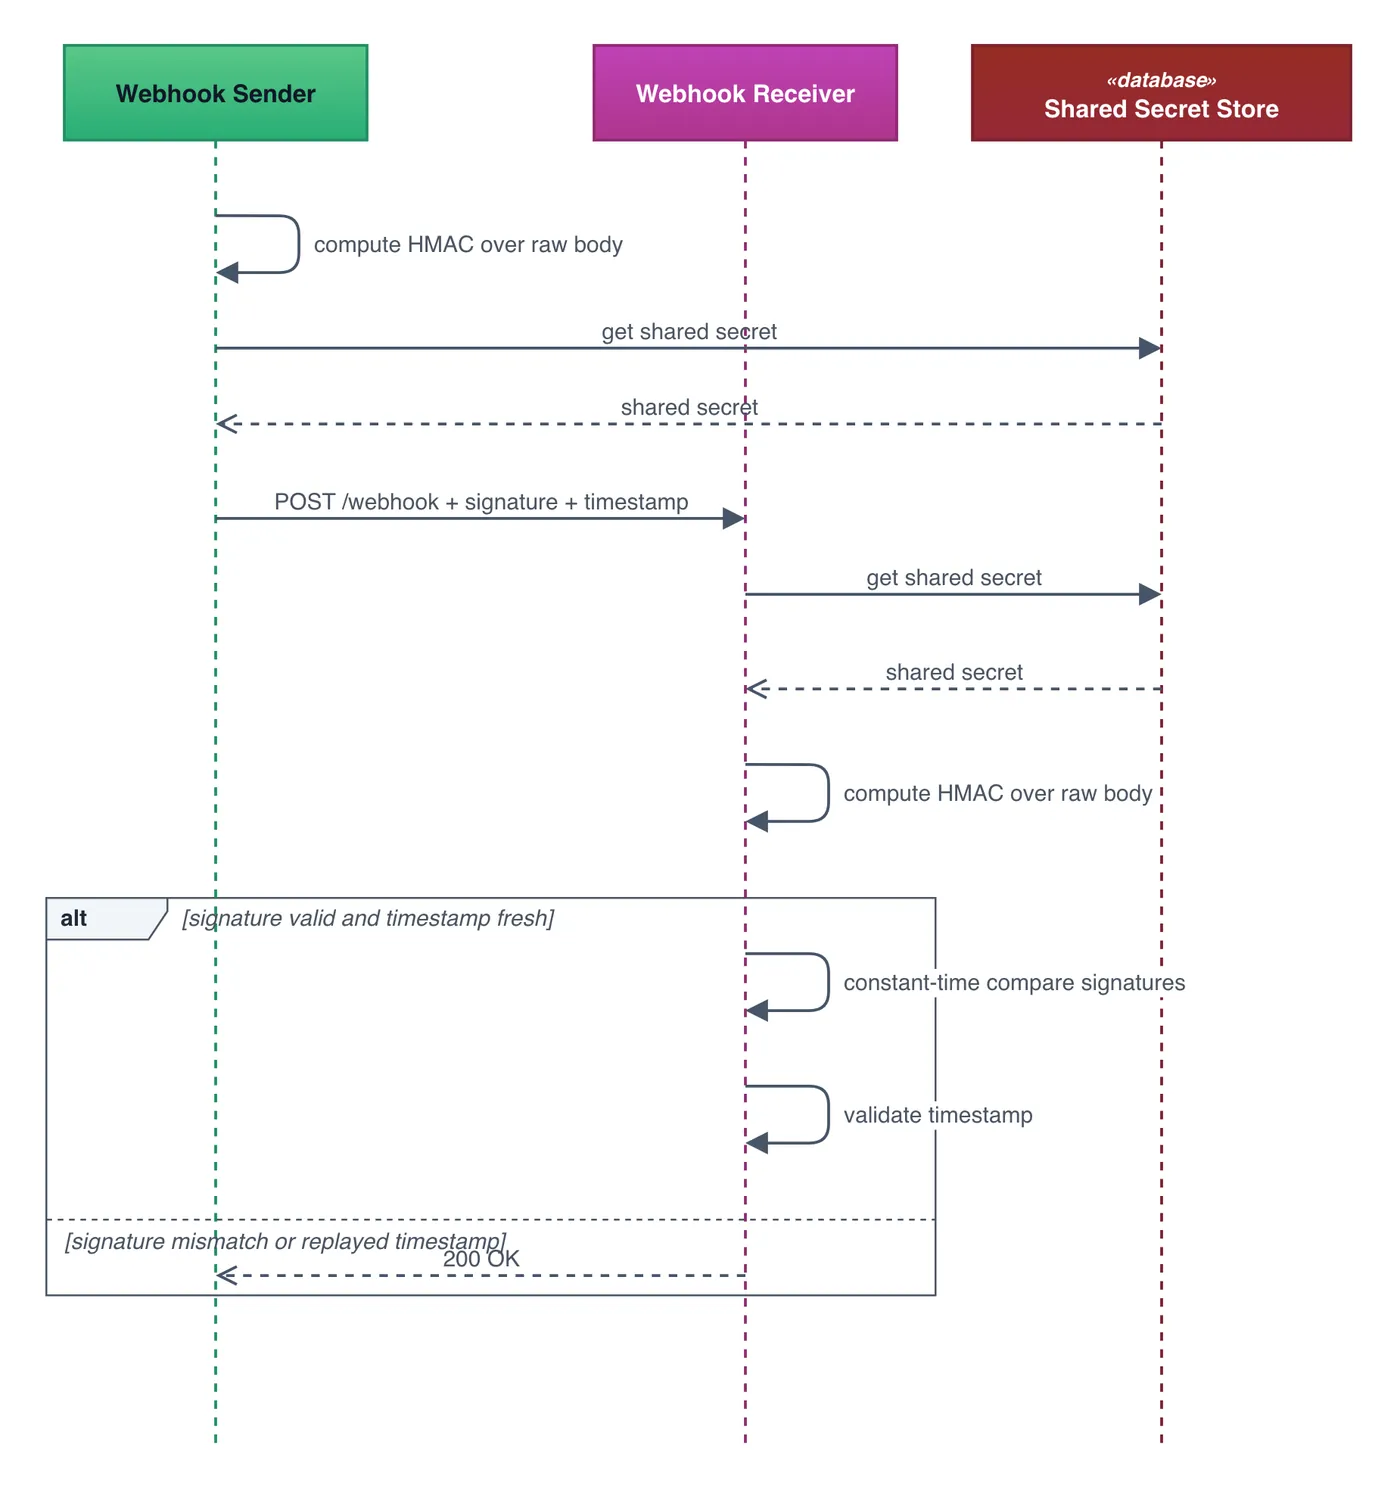
What it shows
- Signatures must be computed over the raw HTTP request body string.
- Compare signatures using constant-time algorithms to prevent timing attacks.
- Validate embedded timestamps to prevent unauthorized replay attacks.
The takeaway
Always verify HMAC signatures with raw bytes and constant-time comparisons before processing webhooks.
- #CyberSecurity
- #Webhooks
- #AppSec
- #BackendDev
- #API
- #SoftwareEngineering