Session Authentication with HttpOnly Cookies
UML Sequence Diagrams · made in Skemio
What it shows
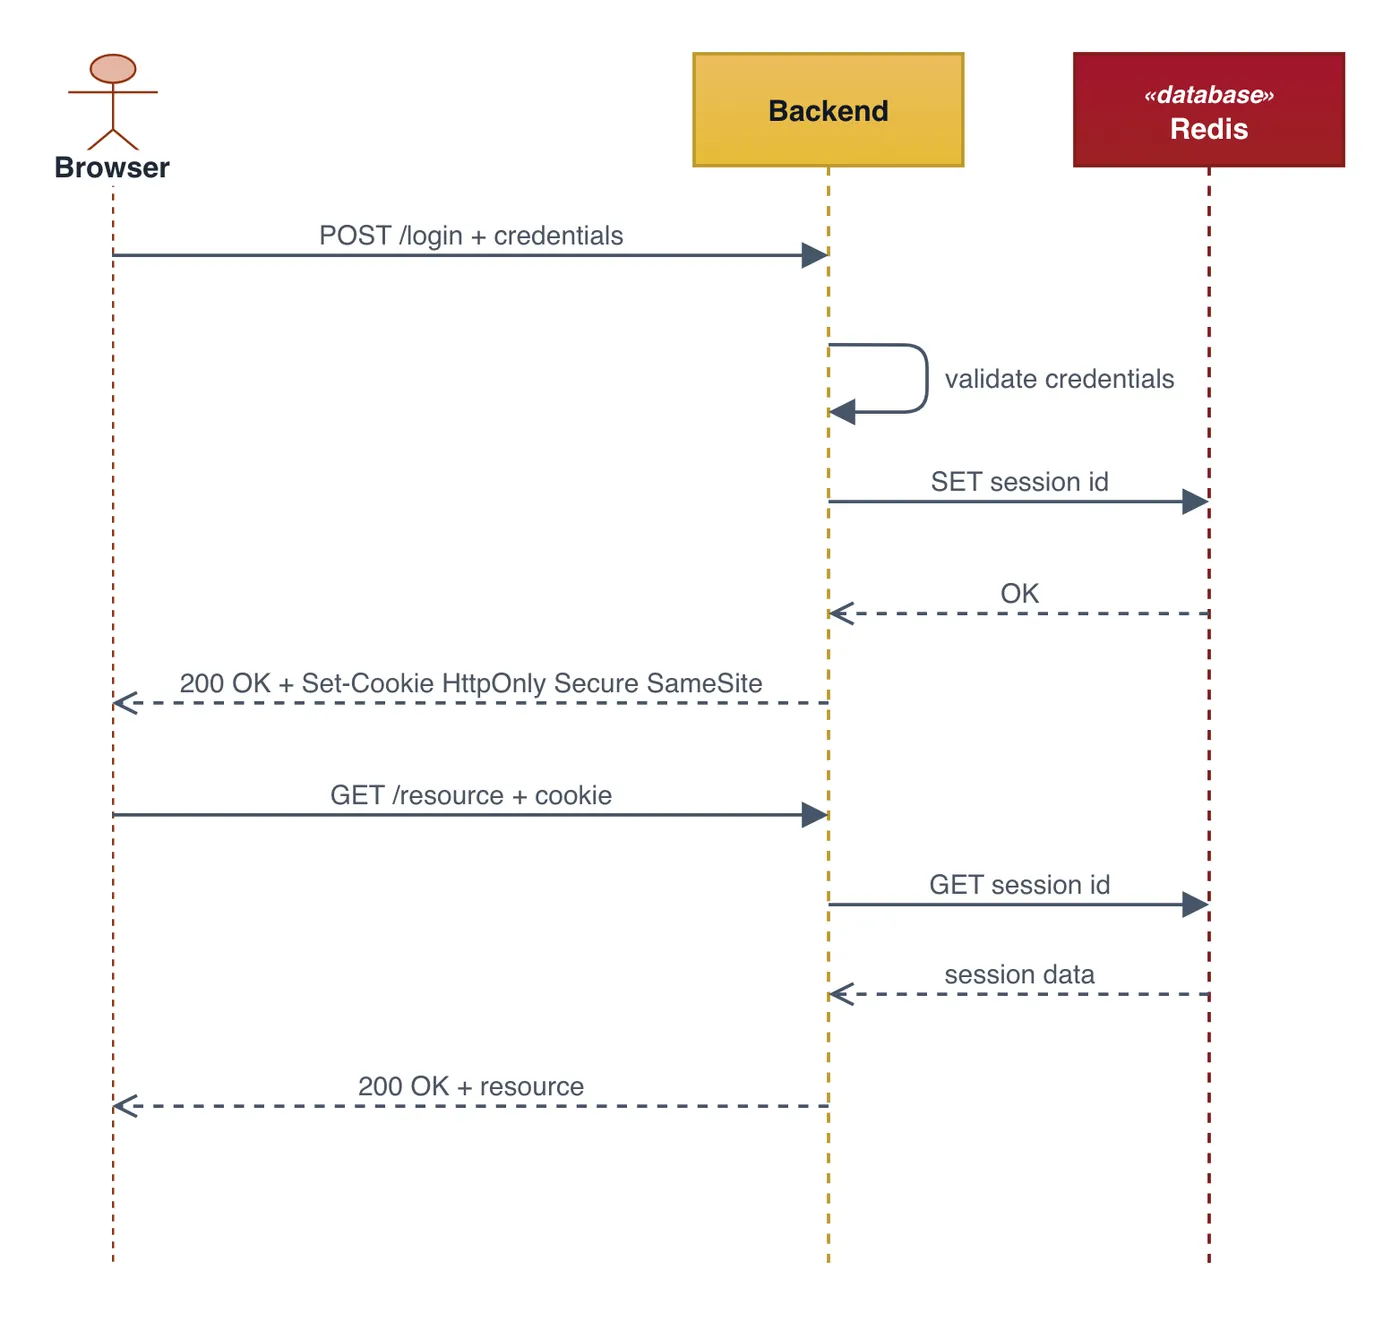
- Backend validates credentials and writes an opaque session id to Redis.
- Browser receives an HttpOnly, Secure, SameSite cookie inaccessible to JS.
- Subsequent requests auto-attach the cookie for O(1) session lookups.
The takeaway
HttpOnly session cookies defend against XSS token theft while enabling instant server-side revocation.
- #WebSecurity
- #Authentication
- #SoftwareEngineering
- #BackendDev
- #InfoSec